Articles

Stay informed on security insights and best practices from Snyk’s leading experts.

Showing 161 - 180 of 379 articles
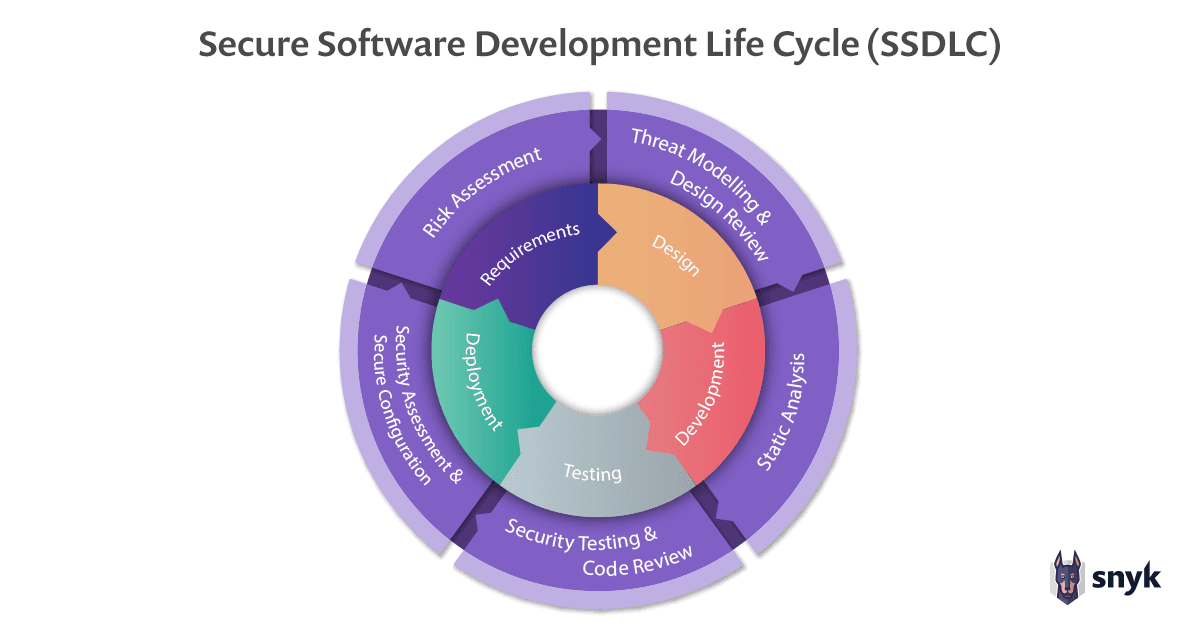
Software Development Life Cycle (SDLC): Phases and Methodologies

Learn more about SDLC (Software Development Life Cycle) phases and methodologies that define the entire software development procedure step-by-step.

feature ctf challenge

Types of CTF challenges

The evolution of CTFs has been a dynamic journey from simple text-based challenges to complex, multifaceted events that test a wide range of cybersecurity skills.

feature ctf challenge

CTF tools

CTFs (Capture the Flag) are competitions where participants try to solve various cybersecurity challenges, such as exploiting vulnerabilities, reverse engineering, digital forensics, and cryptography, to retrieve a "flag." To assist in solving these challenges, there are numerous CTF tools available, and participants typically have a toolkit that caters to the various CTF categories.
blog feature snyk code green

Prompt Injection Exploits Invisible PDF Text to Pass Credit Score Analysis by LLMs

We leverage LLMs for a real-world use case that financial banking applications might use to understand the real business impact of adversarial AI security regarding prompt injection.

feature ctf challenge

CTF platforms & practice

Capture the Flag (CTF) competitions are a popular way for cybersecurity enthusiasts, students, and professionals to test and expand their skills in a gamified environment. Over the years, several platforms have emerged that offer CTF challenges and practice environments. 

Prioritisation header

Complete Guide to Application Security: Tools & Best Practice

Application Security is defined as the actions taken during the development lifecycle of an application to reduce vulnerabilities, improve security, and protect sensitive data.

Compliance FEATURE cropped

The Risks and Impact of Data Leakage: Data Leakage Causes and Prevention

Knowing the risks and impact of data leakage can help protect your organization. Learn more about data leakage, its causes, and how to prevent it here.

RAG vs CAG: Key Differences in AI Generation Strategies

Compare RAG vs CAG AI generation strategies. Learn key differences, trade-offs in accuracy & latency, and choose the best approach for enhancing LLMs with external data.

Understanding the developer attitude to security

Learn why developers adopt security practices, what the blockers are, and what you can do to make it easy for them to stay secure.

Adversarial Inputs to Classifiers Understanding the Threat of Adversarial AI

Agentic AI vs Generative AI

Discover the key differences between agentic and generative AI, and why those distinctions matter for innovation, automation, and security planning.

feature security

8 AI MCP Servers Speeding Up Content Creator Workflows

Discover 8 powerful MCP servers that revolutionize content creation workflows. From video generation to SEO optimization, these AI-powered tools streamline production, boost creativity, and unlock new possibilities for creators.

Package Lock Files blog

Package Hallucination: Impacts and Mitigation

Malicious actors can exploit errors in generative AI tools, and packages can hallucinate. Learn how to identify and mitigate package hallucination attacks with Snyk

What is AI jailbreaking? Strategies to Mitigate LLM Jailbreaking

LLM Jailbreaking happens when adversarial prompts force unintended actions. Discover the best strategies to mitigate and defend against jailbreaking in GenAI models.

feature datacenters black

Stop Data Exfiltration Before It Starts: 9 Proven Strategies

Learn 9 strategies to detect and prevent data exfiltration from insider threats to AI-powered attacks before sensitive data leaves your environment.

feature red team blue team

What is RAG, and How to Secure It

Learn how Retrieval-Augmented Generation improves LLMs with your data. Understand critical RAG security risks & discover best practices to protect your AI.

SAST annoucment

Static Application Security Testing (SAST) Scanning

Learn more about the 7 stages of Static Application Security Testing (SAST) scanning, its pros and cons, and how it can help keep your source code secure.

blog feature parlay announcement

Leveraging Generative AI with DevSecOps for Enhanced Security

Learn about the top advantages of secure AI coding tools for stronger DevSecOps practices with Snyk.

illustration hero ai deepcode

Shadow AI: Unmasking the hidden risks in your Enterprise

Unmask Shadow AI's hidden enterprise risks, from data leaks and compliance woes to security gaps. Learn why it's a threat and how to implement effective governance strategies for safer AI innovation.

blog feature fast sast

StarChat

Discover StarChat, a uniquely tailored internal AI assistant designed to streamline the process of writing StarLang code.

Product Security vs. Application Security: What’s the Difference?

Discover the differences between product and application security to build more secure products and applications.