
Secure AI-written code as the agent writes it
Evo Agentic Development Security (ADS) scans and fixes code inside the agent session, in Claude Code, Cursor, GitHub Copilot, Codex, and more.
Wiz is built for cloud security. Snyk is built for developers, and fixes issues in the IDE, pull request and coding agent session.
"Snyk has helped us make significant strides in shifting security left and increasing developer adoption by integrating security testing directly into developers' IDEs and making security tasks less cumbersome and time-consuming.”


Matthieu Nunick
Security Engineering Manager, Mollie
Leader, 2026 Forrester Wave
for Agentic Development Security Tools


“Every company is moving toward AI, and security has to move with it. Snyk is ready to support our AI initiatives by protecting us as we adopt and experiment with AI. That's exactly the kind of partner we want for this next phase.”
Leon Direito
CISO, Yalo
“The biggest benefit of Snyk has been the ease of use. I would definitely recommend Snyk, especially if you have issues with dependency management.”
Chitra Dharmarajan
VP, Security & Privacy Engineering, Okta
"We want our developers to be enabled with all the metadata about their known CVEs… and Snyk helps us take a systematic and methodical approach to triage the impact of CVEs in our codebase."
Ethan Willer
Senior Information Security Analyst, Seismic
“Compared to our previous tooling, Snyk’s scanning is 2x faster and much more integrated to their tooling and processes.”
Eric Cheng
Digital Solutions Architect, Komatsu
Read Komatsu's case study
“To innovate securely with AI, companies need to adopt AI thoughtfully and delegate tasks that AI can do best. And I believe Snyk will support that by delivering industry-leading AI models and keeping them on the bleeding edge of security innovation.”
Ramon Borunda
Sr. Cloud Platform Engineer, Skechers, USA
| Features | Snyk | Wiz |
|---|---|---|
| AI-written code | ✔ Snyk Studio scans and fixes in the agent session, as code is written. | ✘ Plugins scan at file save, pre-commit, and pre-push. |
| Agent governance | ✔ Evo Agentic Development Security blocks unapproved MCP calls before the tool runs. | ✘ Inventories agents and MCP servers and notifies. No pre-execution block published. |
| Agent supply chain | ✔ Evo Agentic Development Security scores MCP servers, tools and skills before agents use them. | ✘ No published security score. |
| Developer workflow | ✔ Findings and one-click fixes in IDE, SCM, CLI, CI/CD and AI coding tools. | ✘ Findings start in the Wiz console; IDE plugins pull issues to developers. |
| AppSec analyst standing | ✔ Leader in 2026 Forrester ADS Wave, 2026 IDC DAST MarketScape, and 2025 Gartner Magic Quadrant, Application Security Testing. | ✘ Not named in any of these 2026 reports. |
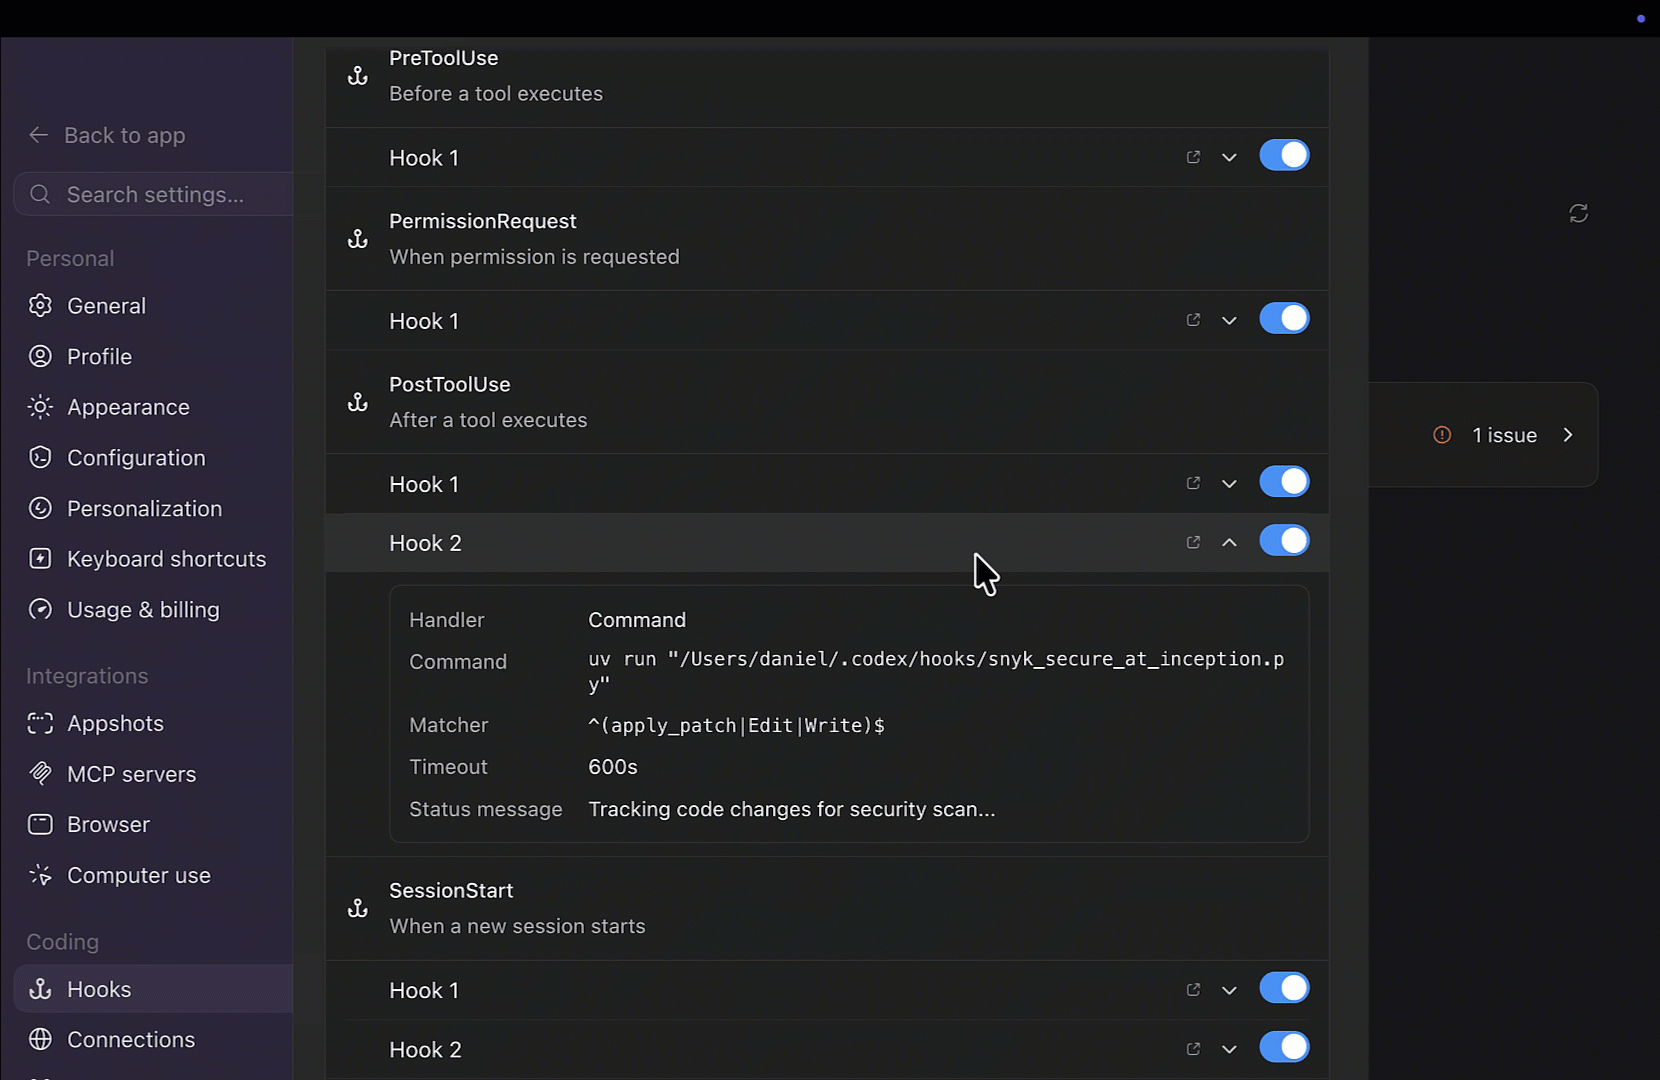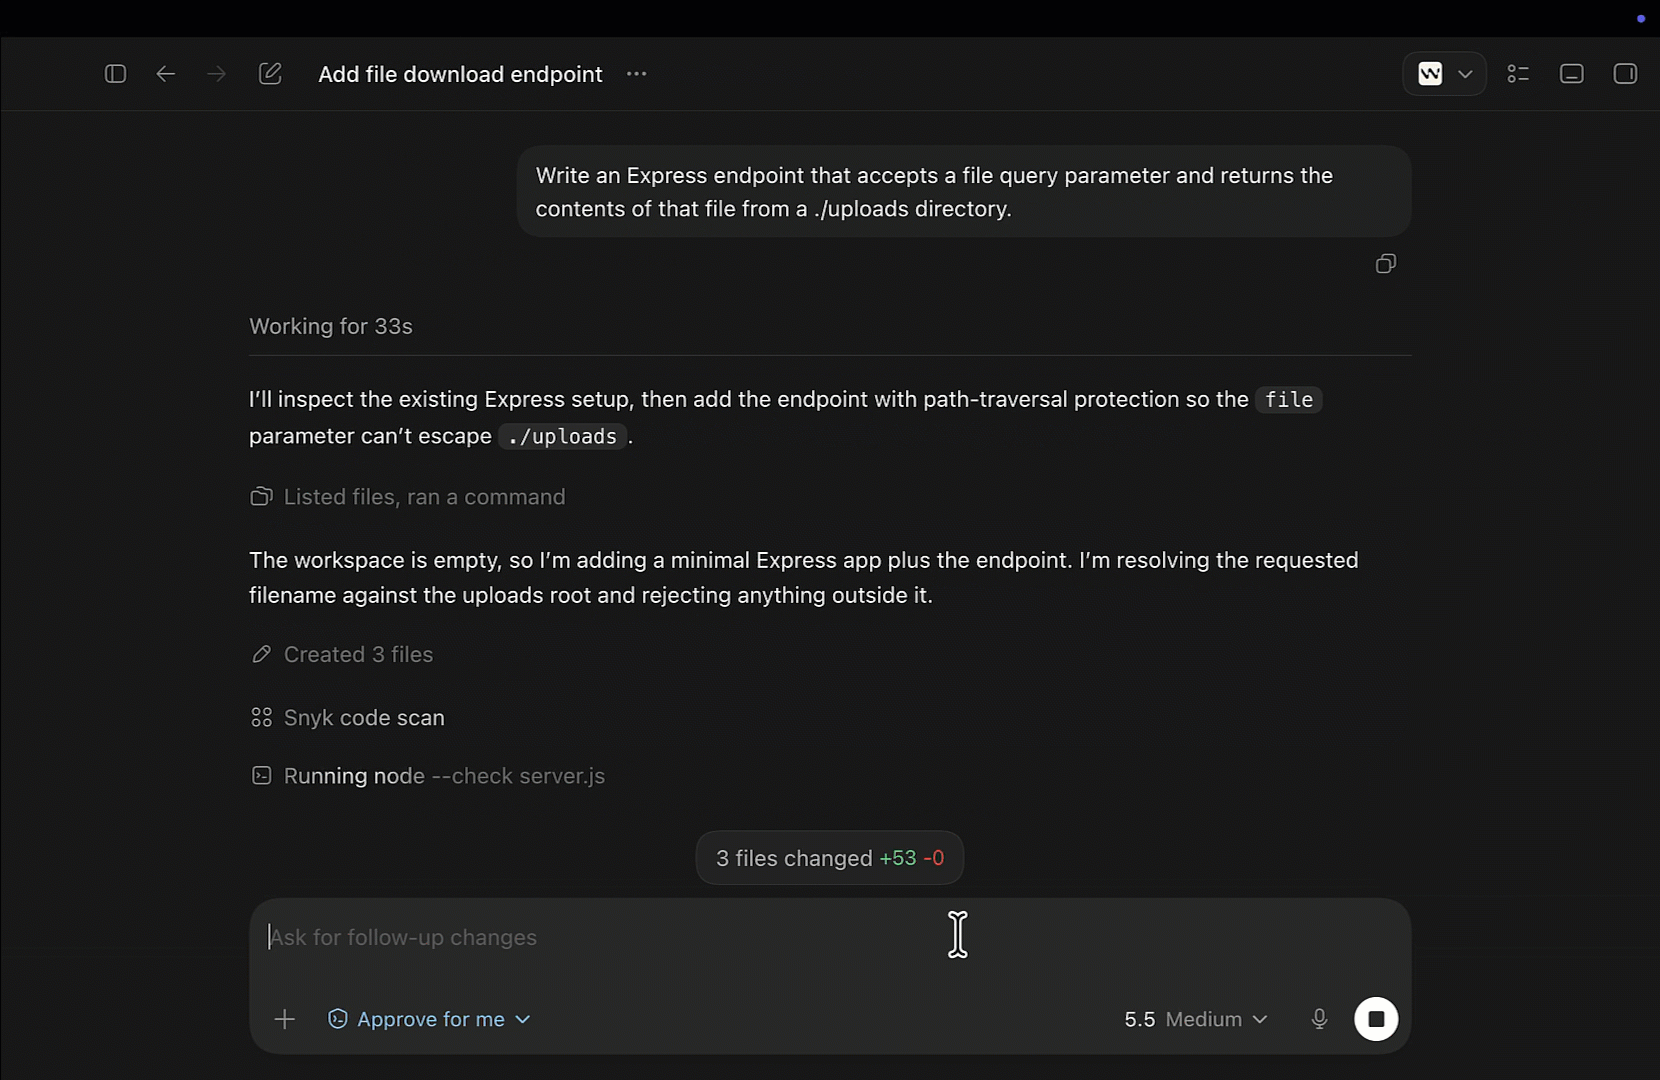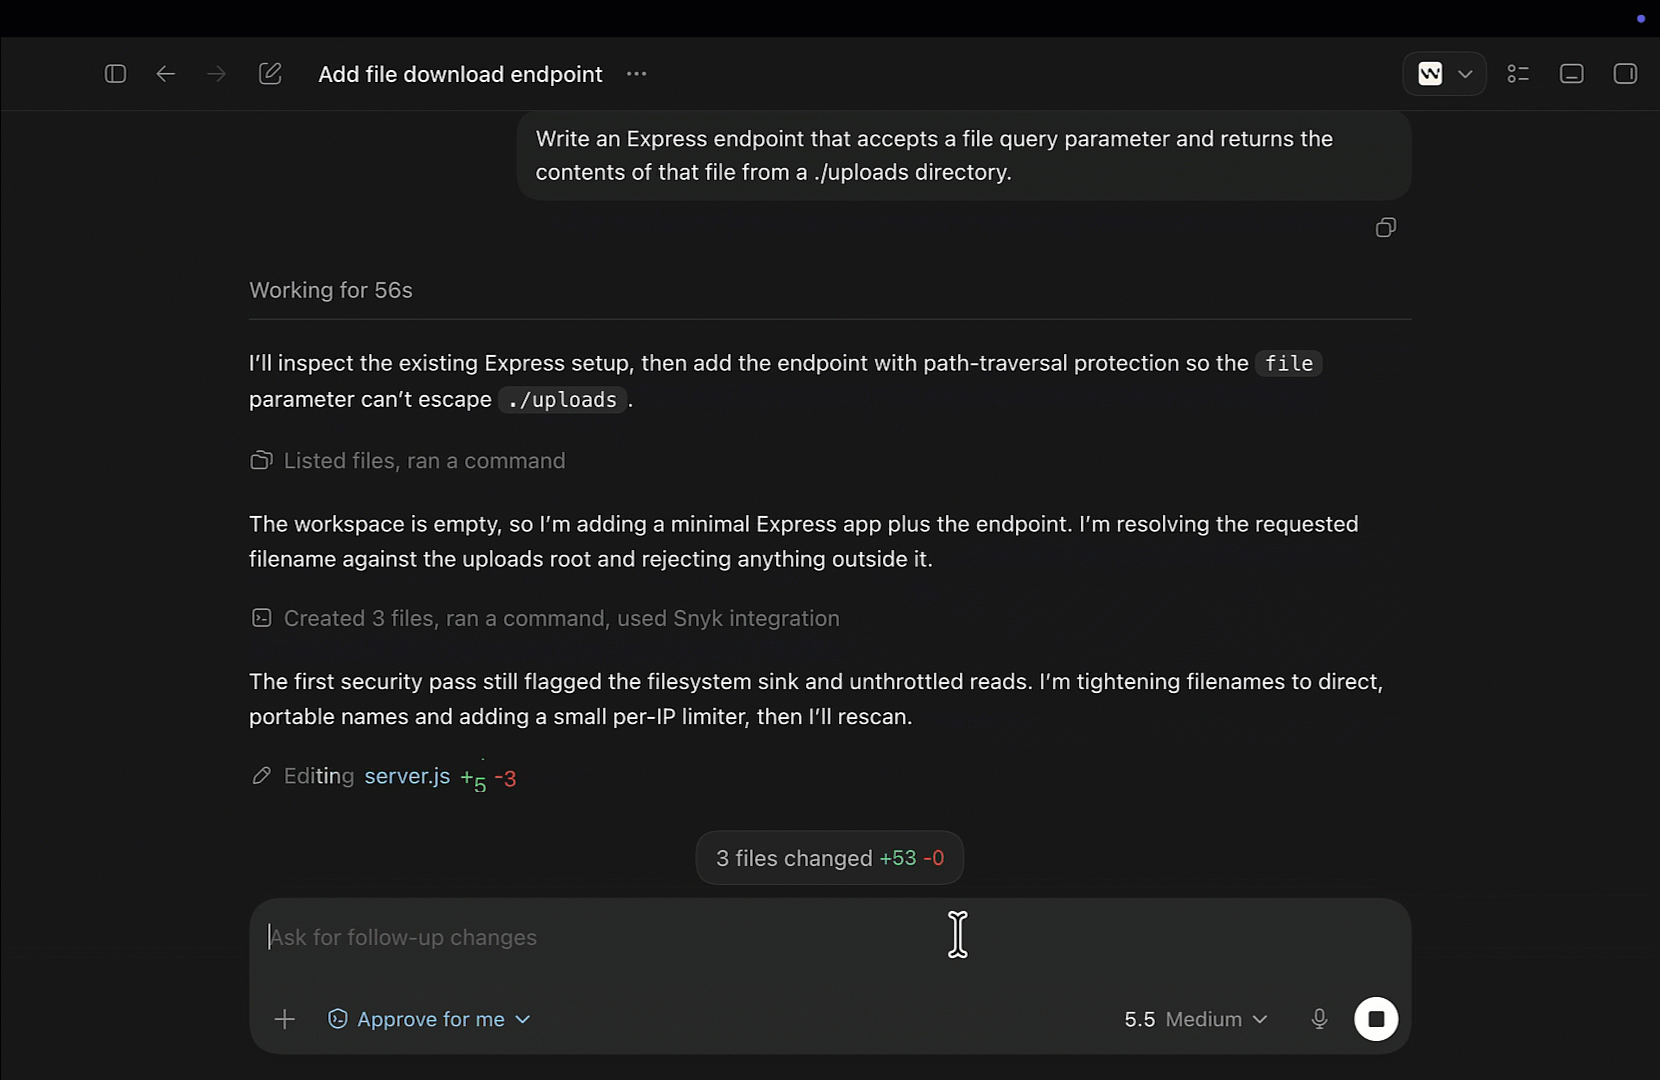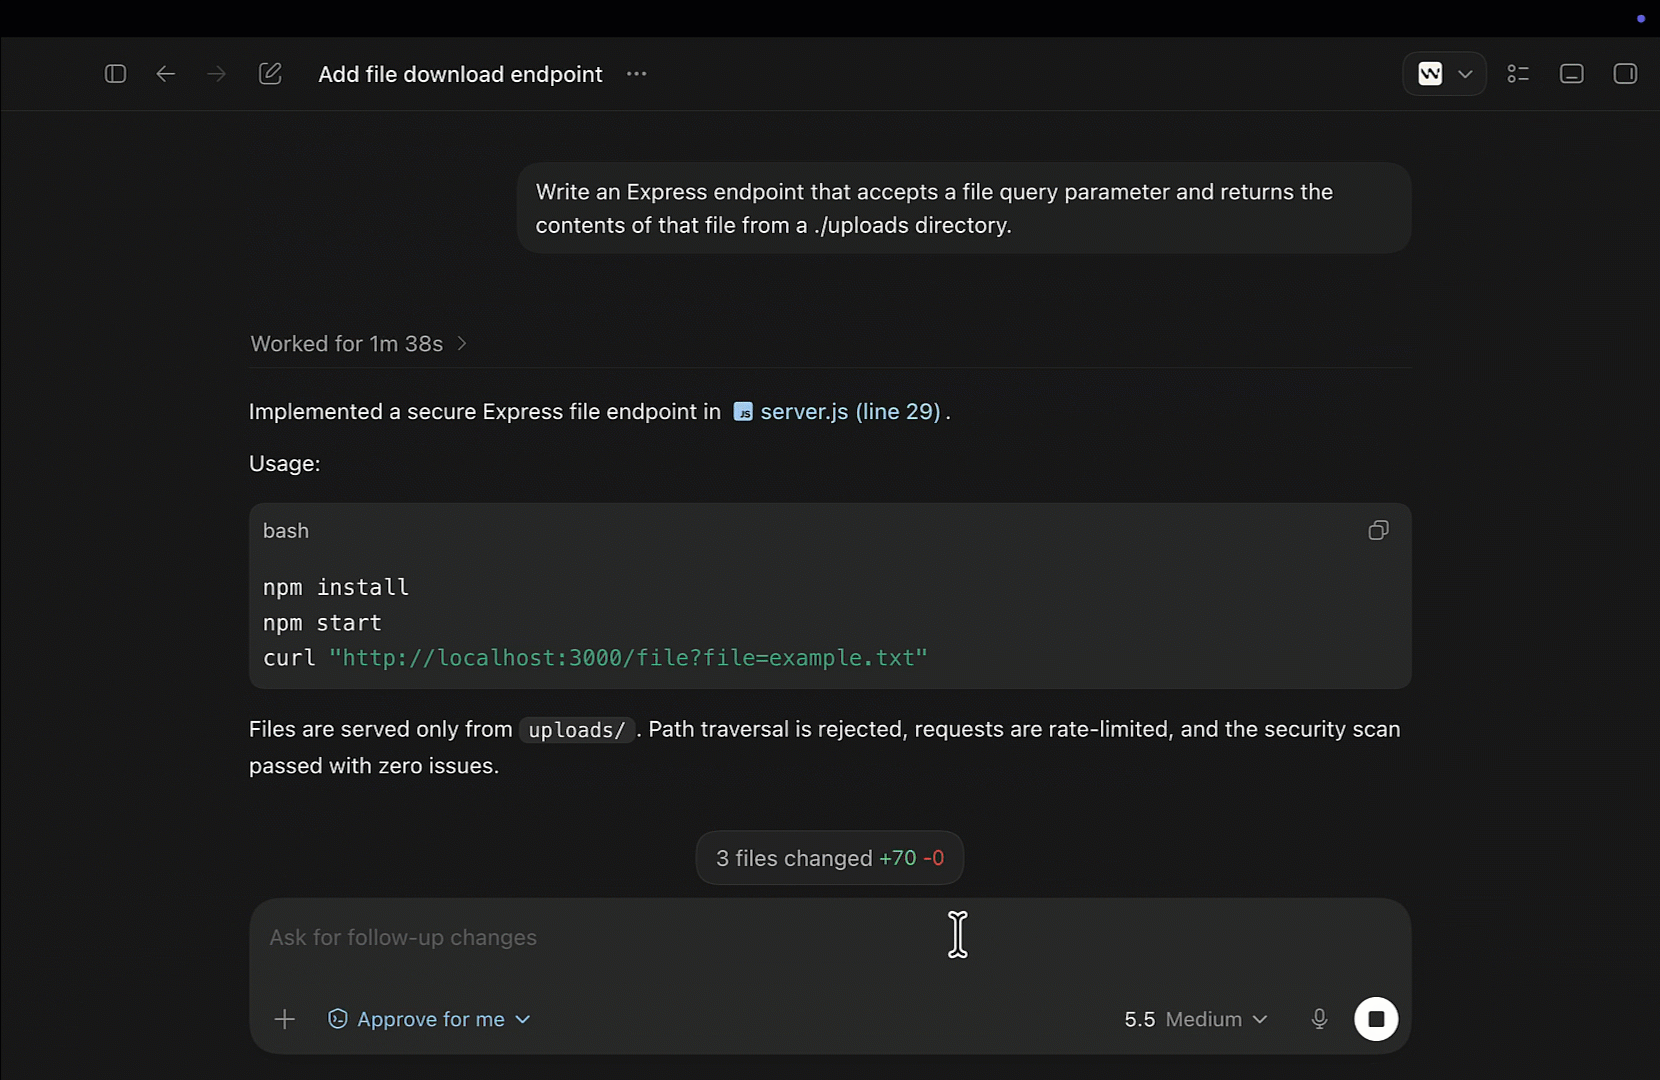
Evo Agentic Development Security (ADS) scans and fixes code inside the agent session, in Claude Code, Cursor, GitHub Copilot, Codex, and more.

Evo Agentic Development Security scores MCP servers, tools, and skills before agents use them, and blocks calls to unapproved MCP servers before the tool runs.

Findings and one-click fixes appear in the IDE, pull request, CLI, and CI/CD, where developers already work. Wiz surfaces findings in a security console and routes them back to developers.
Wiz is a cloud security platform, and Snyk is an application security platform built for developers. Snyk puts findings and one-click fixes in the IDE, pull request, CLI, and CI/CD, and secures code as AI agents write it.
Snyk covers SAST, SCA, containers, IaC, and DAST with Snyk Code, Snyk Open Source, Snyk Container, Snyk IaC, and Snyk API & Web.
Teams switch from Wiz to Snyk when code risk has to be fixed in developer workflows, not just found. Snyk puts findings and one-click fixes in the IDE, pull request, CLI, and CI/CD, and secures code as AI coding agents write it. Per the Forrester Wave, Snyk is a leader in Agentic development security, which secures the code, tools, and actions of AI coding agents.
Snyk Studio scans and fixes AI-written code inside the coding agent session, as the agent writes it, so fixes land before the commit. Wiz Code plugins scan at file save, pre-commit and pre-push. In Wiz’s documented flow, the developer applies the fixes. Evo Agentic Development Security also blocks unapproved MCP calls before the tool runs.
288% ROI and $15.5M NPV over three years
with a 52% reduction in mean time to remediation. Forrester Total Economic Impact study.