Articles

Stay informed on security insights and best practices from Snyk’s leading experts.

Showing 141 - 160 of 379 articles

Enterprise security: How to stay secure at enterprise scale

Enterprise security is the use of technologies, practices, and processes to protect digital assets, systems, and data from threats and vulnerabilities.

How is AI being used in cybersecurity?

Learn how the emergence of AI is changing organizations' approaches to cybersecurity, leveraging different AI models to improve the efficiency of cybersecurity programs.

blog feature supply chain sbom

A Beginner's Guide to Visually Understanding MCP Architecture

A beginner's guide to understanding Model Context Protocol (MCP) architecture visually. Explore MCP Hosts, Clients, Servers, transport types, and how MCP extends LLMs beyond function calling & REST APIs.

feature ctf challenge

Gaining transferable security skills with CTFs

prioritize the security backlog

Beyond Predictability: Securing Non-deterministic Generative AI in Today's Cyber Landscape

Explore how to secure non-deterministic generative AI systems in an evolving cyber threat landscape. Learn key risks, real-world implications, and expert strategies for resilient AI deployment.

Cloud Compliance Tools Guide

When choosing a cloud compliance tool, consider capabilities such as policy as code and historical reporting to help maintain and verify your compliance.

Ethical Hacking: Vulnerability Disclosure Program (VDP) Vs Bug Bounty (BB)

How does a bug bounty (BB) program compare to other vulnerability disclosure programs (VDP)? Learn how enterprises are using VDPs to help secure their applications.

snyk code blog

Understanding Security Automation

Learn more about security automation, a practical necessity for any successful software operation. Identify incoming cyberthreats and prioritize remediation actions.

DevSecOps Culture

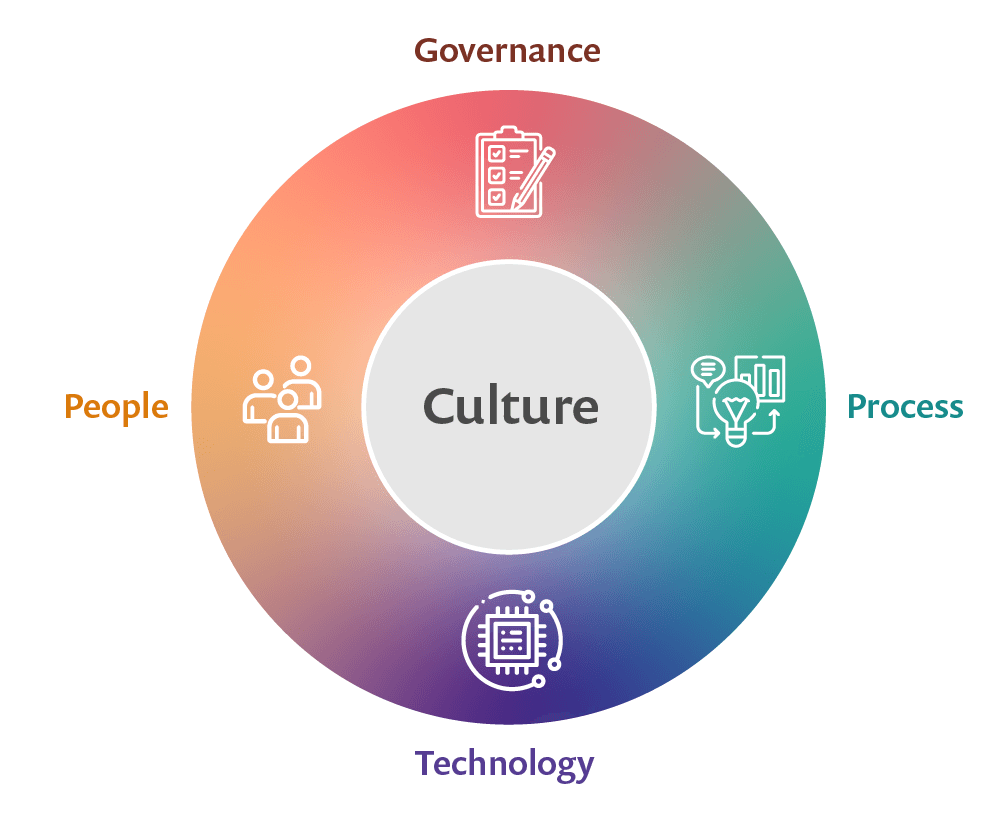
Online media and marketing are filled with terms like DevSecOps methodology, DevSecOps model, or DevSecOps techniques. However, in order to be successful, organizations must understand that DevSecOps is first and foremost a culture. DevSecOps culture focuses on uniting the normally siloed roles of Development, Security, and Operations into a collaborative shared-responsibility paradigm. It seeks to break down barriers of finger pointing and deflection. Instead, it aims to build empathy and common goals among various disciplines within the organization.

feature snyk iac green

Cloud security posture management explained

When many companies move to the cloud, they assume the cloud provider – whether it’s Amazon Web Services (AWS), Google Cloud, Microsoft Azure or any other – is completely responsible for cloud security.

The Essential Guide to AI Bills of Materials (AIBOMs)

This guide is your one-stop shop on AI Bill of Materials (AIBOMs). Learn how to build an inventory of your AI model.

Building a Security News Summary with CrewAI AI Agent

Learn how to create an AI agent using the CrewAI framework to curate and summarize critical security vulnerabilities from the Snyk database. Automate your security news feed and stay informed effortlessly.

What is enterprise-grade security?

By embracing an enterprise-grade approach, businesses can ensure end-to-end security throughout their software development journey

Ethical Hacking: Reporting Your Findings

Ethical hackers need to share the information they discover through detailed reports. Learn about the different report types, and how to construct them.

Risk-Based Vulnerability Management (RBVM): What is it & how to implement

Risk-based vulnerability management (RBVM) is a relatively new AppSec practice that empowers organizations to see their risk in context and prioritize the most critical fixes.

blog feature fast sast

How to Secure Your GitHub Actions Workflows with Snyk to Enhance JavaScript Security

Snyk provides a pre-built custom Snyk GitHub Actions workflow that you can add to your CI and saves you the trouble of managing the vulnerability scans using the Snyk CLI directly.

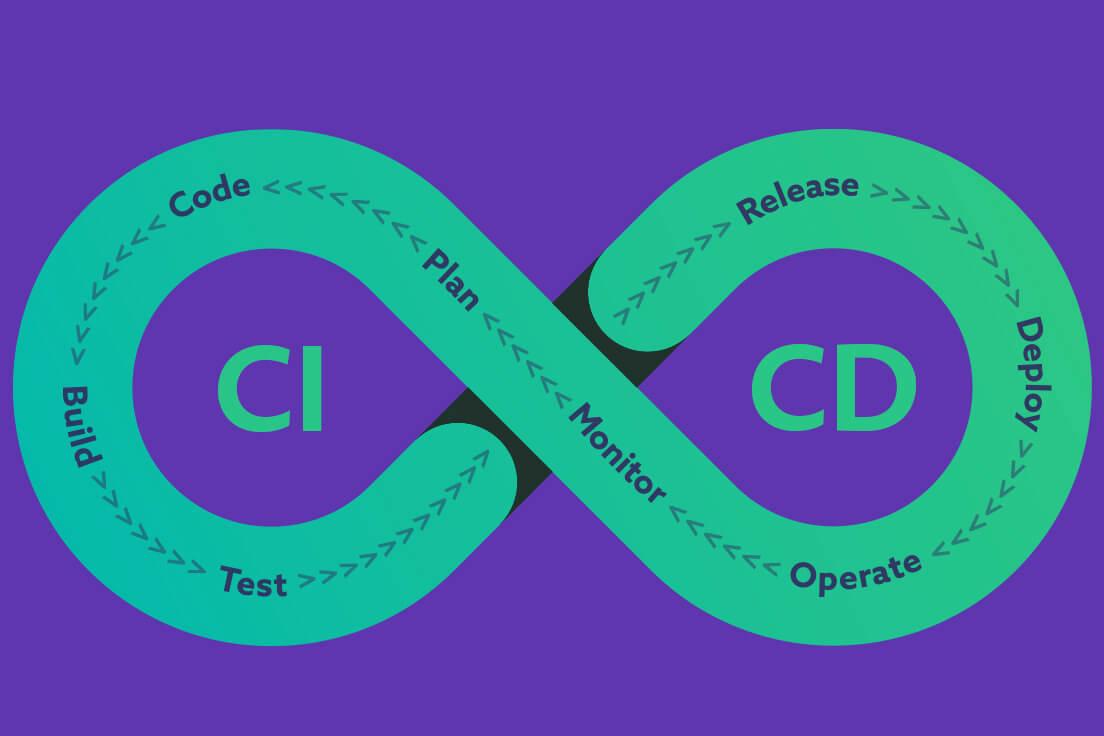
What is CI/CD? CI/CD pipeline and tools explained

Learn more about CI/CD continuous integration and continuous delivery, CI/CD pipeline, and framework. CI/CD as the foundation for DevSecOps.

Understanding development teams

Driving developer adoption of security tools and practices requires empathy for and understanding of your development teams.

Cloud Security Automation

Organizations working towards adopting cloud computing report that security and compliance are two of the top three barriers they face: 35% of cybersecurity professionals stated security is their biggest barrier, while 31% reported compliance (Statista).

blog feature multithreading

Guide to Software Composition Analysis: 5 key challenges of SCA

The code driving many—in fact, most—applications today includes open source components.