Report
Snyk named a Leader in The Forrester Wave™: Agentic Development Security Tools (Gated)
Learn why Snyk was named a Leader in The Forrester Wave™: Agentic Development Security Tools, Q4 2026.
Cheat Sheet
Cheat Sheet
Video
Report
Showing 49 - 72 of 756 resources
Top 9 Claude Skills for Cybersecurity, Hacking, and Vulnerability Scanning
From YARA rule authoring to OWASP compliance checks, these 9 Claude Skills give security professionals AI-powered workflows for penetration testing, code auditing, and vulnerability detection.
Tauri Footguns: 5 Common Security Misconfigurations That Ship by Default
Tauri promises a more secure alternative to Electron for desktop apps, but several default configurations and common patterns quietly undermine its security model. We break down five footguns that developers should watch for.

The state of secrets: Why 28 million credentials leaked on GitHub in 2025, and what to do about it
28.65 million hardcoded secrets were added to public GitHub in 2025. This guide covers the full landscape of credentials management: why secrets leak, what tools catch them, and how to build a layered defense that works, from pre-commit hooks to AI-aware scanning.
Trivy GitHub Actions Supply Chain Compromise
Attackers compromised 75 version tags of the popular Trivy GitHub Action, turning the security scanner into a credential-stealing tool. Learn how the two-stage attack chain unfolded, whether you're affected, and how to secure your CI/CD pipelines against GitHub Actions supply chain attacks.
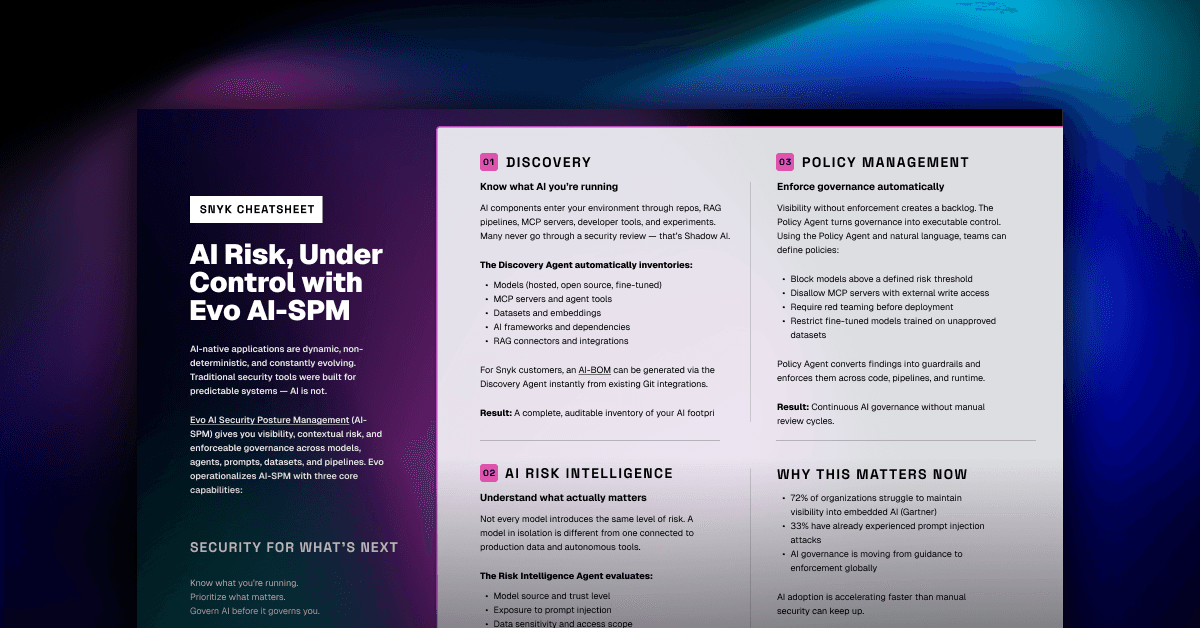
AI Risk, Under Control with Evo AI-SPM
Top 8 Claude Skills for Entrepreneurs, Startup Founders, and Solopreneurs
From SaaS financial modeling to conversion copywriting and product-market fit research, these 8 Claude Skills give entrepreneurs AI-powered workflows for launching and scaling a business.
Inside StegaBin: How a DPRK Steganography Campaign Generated Headlines
North Korean hackers published 26 malicious npm packages using Pastebin steganography for C2. It made headlines everywhere. We checked the data: zero real-world impact. Here's what the campaign actually did, and what it tells us about the real risk of malicious package campaigns.
CVE-2026-29000: How a Public Key Breaks Authentication in pac4j-jwt
CVE-2026-29000 is a CVSS 10.0 authentication bypass in pac4j-jwt that lets attackers forge admin tokens using only the server's RSA public key. Learn how the vulnerability works, whether you're affected, and how to fix it.
AI Radar: February Edition
Earn CPE credits! Each session provides a deep dive into real-world issues and offers actionable insights to safeguard your applications. We bridge the gap between traditional security and the new frontier of AI-native applications, ensuring your team can innovate without compromise.
Accelerating Public Sector Modernization with Secure AI-Driven Migration
Learn how generative AI accelerates legacy application migration for the public sector—and how Snyk secures AI-generated code, dependencies, containers, and cloud infrastructure from code to cloud.
DAST vs. Penetration Testing: 5 Key Differences
Deciding between DAST and penetration testing is vital for securing modern APIs and microservices. Learn how to combine these methodologies to build a robust, layered security strategy that protects your entire application portfolio.
Top 8 Claude Skills for UI/UX Engineers
Explore the top Claude Skills transforming UI/UX engineering by automating repetitive tasks like accessibility audits and component scaffolding. Discover how to streamline your workflow and focus on the creative decisions that truly matter.
Top 8 Claude Skills for Developers
From Manus-style task planning to Terraform code generation and Core Web Vitals optimization, these 8 Claude Skills give developers repeatable AI-powered workflows for real engineering work.
Six Principles for Rethinking DevSecOps for AI
The 6 factors are: Developer-First AI Security, Secure AI by Design, Shared AI Accountability, Automated AI Security, AI-Specific Intelligence, and AI Governance & Continuous Improvement
Your AI "Skills" Are the New Agentic Attack Surface
As AI moves beyond simple chat to autonomous execution, the skills powering these agents have emerged as a dangerous new attack surface. Learn how to protect your organization from malicious AI agent tools while maintaining development velocity in the age of agentic workflows.

Anthropic Just Launched Claude Code Security. Here's Why That's Great News for the Industry
Anthropic's launch of Claude Code Security is sparking headlines about the end of traditional security, but the real story is about the shift from detection to automated remediation. This move validates a layered security approach that combines AI reasoning with deterministic analysis to protect the modern software supply chain.