
8 Azure Repos Security Best Practices

Written by

Edward Thompson
Cheat Sheet Azure Repos Tips

May 6, 2019

0 mins read

In this cheat sheet, we’ll cover how you can be more secure as an Azure Repos user or contributor. Some of it is specific to Azure Repos, but a lot of it is also useful for other Git and non-Git repositories as well.

Let’s get started with our list of 8 Azure Repos security best practices:

  1. Never store credentials as code/config in Azure Repos

  2. Remove sensitive data in your files and Azure Repos history

  3. Tightly control access

  4. Add a SECURITY.md file

  5. Use Personal Access Tokens

  6. Provide granular permissions and groups for users

  7. Add security testing to Pull Requests

  8. Rotate SSH keys and personal access tokens

If you haven’t done so yet, make sure you download this cheat sheet now and pin it up, so your future decisions are secure decisions.


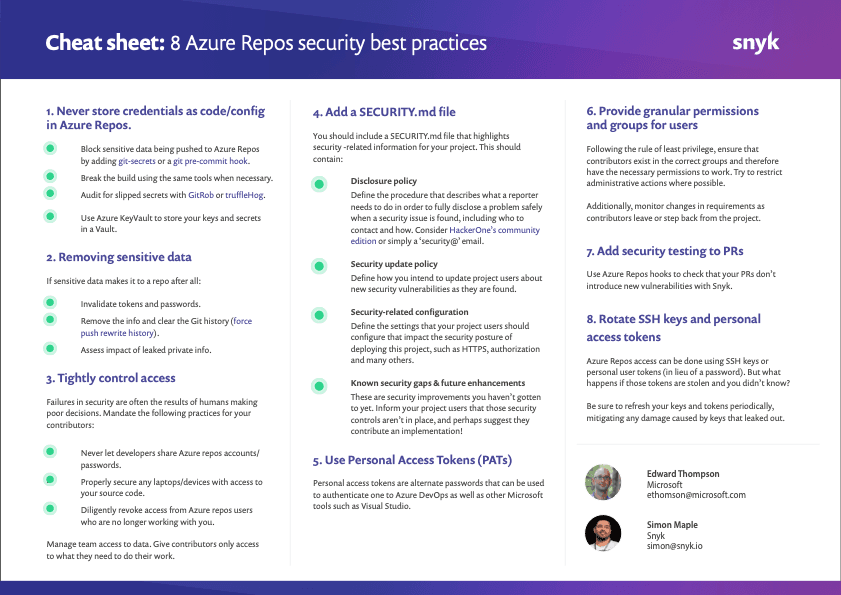
Cheat sheet titled “8 Azure Repos security best practices,” with guidance on credentials, access control, security testing, and SSH keys.

Read more

blog feature snyk container custom base recommendations
Blog

Introducing Evo Agentic AppSec: Security That Keeps Up With AI Development

AI-driven development is outpacing traditional security workflows. Snyk’s Agentic AppSec uses security agents to find, fix, and verify vulnerabilities continuously, while humans set the bar.

feature insights context
Blog

Autonomous Attacks Are Already Here. The Defense Has to Match Their Speed.

Autonomous attackers are shrinking the window for defense. Learn how continuous discovery, remediation, validation, and prevention can help security teams keep pace.

Blog

Evo ADS Govern Agent Behavior Goes GA: Bringing MCP Usage Under Control

Evo ADS Govern Agent Behavior is now generally available, starting with MCP Governance. Discover, approve, monitor, log, and block MCP server usage across leading AI coding agents.

