Add security testing to pull requests in Azure Repos

Written by

Edward Thompson

Blog Graphics

May 6, 2019

0 mins read

This post highlights best practice #7 — add security testing to PRs — from our series of 8 security best practices for Azure Repos.

Adding security testing to pull requests in Azure Repos

By adding Snyk’s native integration with Azure Repos, each pull request will be tested to ensure new vulnerabilities aren’t introduced into the code base. Policies can be defined to configure the severity level of a vulnerability that fails the merge. The following image displays a failed PR due to new vulnerabilities that it would have added:
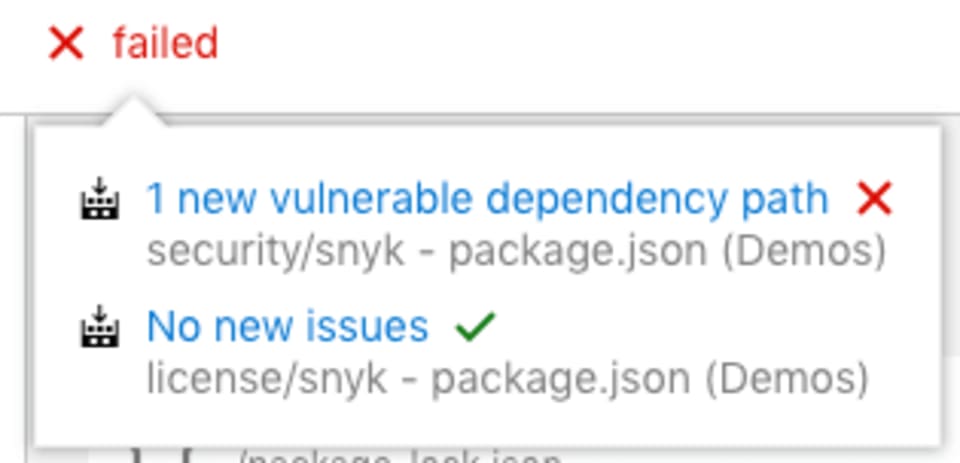
Azure Repos pull request security check showing one new vulnerable dependency path and no new issues

If Snyk finds a vulnerability it provides developers with the needed tools in order to triage and fix the vulnerabilities. Snyk calculates the required fix for both direct and transitive dependencies and automatically populates a fix pull request with the required upgrades or patches, all from within the Azure Repos workflow. The following image displays a fix PR created by Snyk.
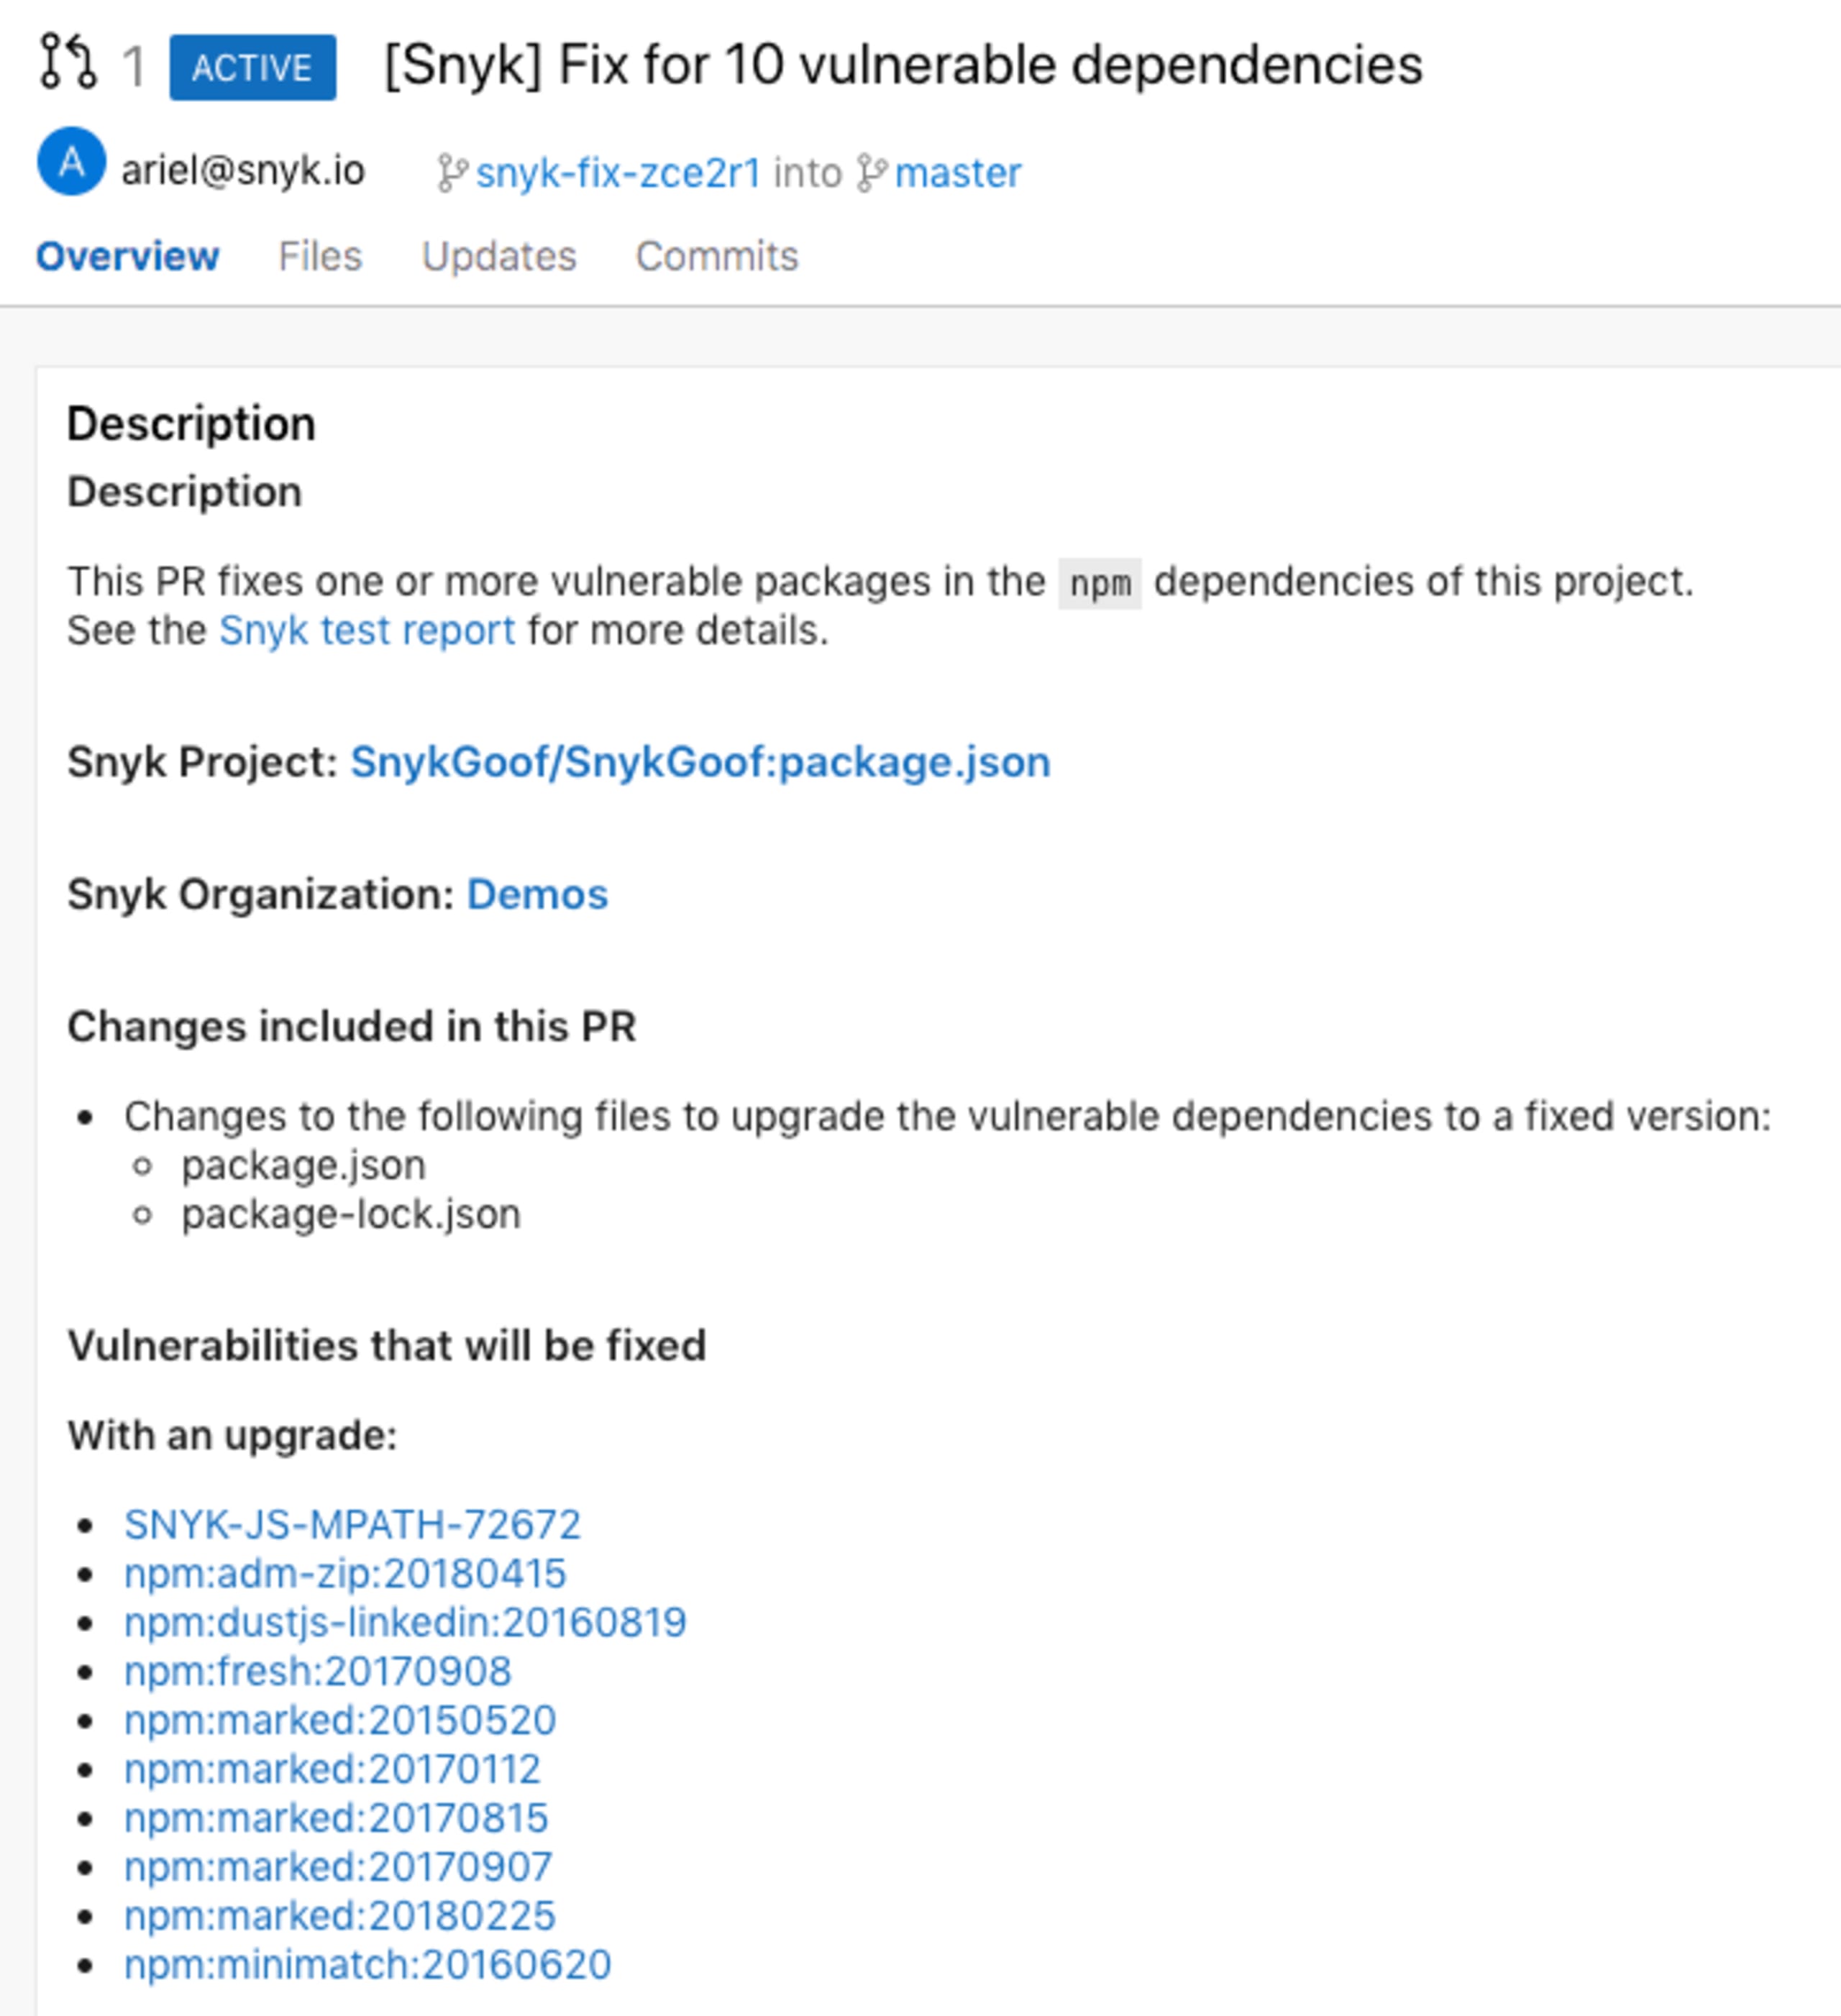
Azure Repos pull request showing a Snyk fix for 10 vulnerable npm dependencies, including updated package files and vulnerability links.

* The functionality of Fix PR and testing new PRs is in closed beta. Please contact us if you would like to join it.


Continue reading the list of 8 security best practices for working with Azure Repos:

  1. Never store credentials as code/config in Azure Repos

  2. Remove sensitive data in your files and Azure Repos history

  3. Tightly control access

  4. Add a SECURITY.md file

  5. Use Personal Access Tokens

  6. Provide granular permissions and groups for users

  7. Add security testing to Pull Requests

  8. Rotate SSH keys and personal access tokens

If you haven’t done so yet, make sure you download this cheat sheet now and pin it up, so your future decisions are secure decisions.


Cheat sheet titled “8 Azure Repos security best practices,” with guidance on credentials, access control, security testing, and SSH keys.

Posted in:

Read more

Blog

JPMorgan Just Published a Cyber To-Do List and Snyk Covers 8 of the 10 Items. How do you stack up?

JPMorganChase published a 10-point cyber resilience checklist. See how Snyk covers 8 of the 10 actions and where it fits in your security stack.

feature datacenters black
Blog

How Snyk Helps Federal Agencies Prepare for the Genesis Mission Era of AI-Driven Science

Snyk helps Federal Agencies secure software for the White House's Genesis Mission, accelerating AI-driven science. Implement Secure by Design for the supply chain, cloud, and pipelines.

feature red team blue team
Blog

Ensuring comprehensive security testing in DevOps pipelines

Learn how to integrate comprehensive security testing into DevOps pipelines to protect your entire software development lifecycle.