Report
Snyk named a Leader in The Forrester Wave™: Agentic Development Security Tools (Gated)
Learn why Snyk was named a Leader in The Forrester Wave™: Agentic Development Security Tools, Q4 2026.
Cheat Sheet
Cheat Sheet
Video
Report
Showing 697 - 720 of 756 resources
Top SAST and SCA Considerations for Security Professionals
Download this guide to learn about the critical aspects of a well-rounded AppSec program that security professionals should consider when choosing (SAST) and (SCA) tools.
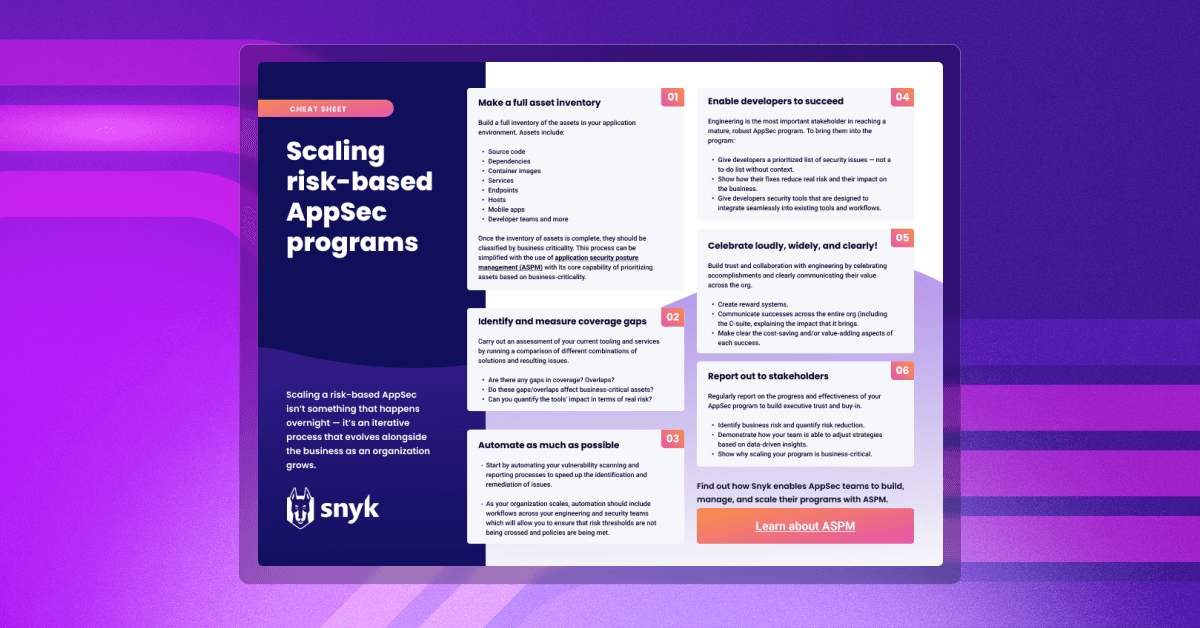
6 Steps for Scaling Risk-Based AppSec Programs
Looking to strengthen your application security posture at scale? Learn how to define, manage, and scale your application security program with end-to-end visibility across your applications, coverage, and governance through these 6 key steps.

How to Perform an Application Security Gap Analysis
Curious to learn how an Application Security Gap Analysis can help you identify areas of weakness within your AppSec program? In this guide we'll walk through the steps to run an Application Security Gap Analysis.
Reporting AppSec Risk up to Your CISO
Level up your security reporting with meaningful insights on the health and growth of your application security program, while ensuring risks posing the greatest threat to the business are resolved quickly and without disruption to developer workflows.
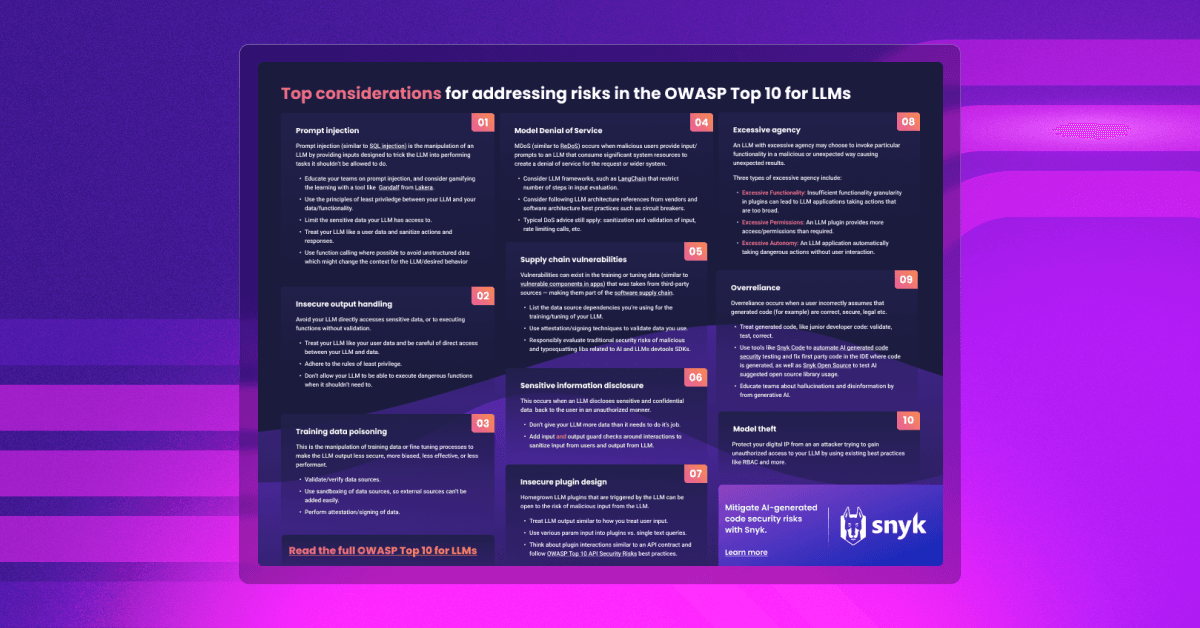
Top Considerations for Addressing Risks in the OWASP Top 10 for LLMs
In this cheatsheet, we’ll look at what OWASP considers the top 10 highest risk issues that applications face using this new technology.
Zero-Day Vulnerability Playbook
In this guide, we’ll cover the basics of zero-days and then provide a playbook that your team can use to prepare for any zero-days on the horizon.
Driving Developer Adoption of Security Tools
Download this cheatsheet to learn how to drive developer adoption of security tools.
Buyer's Guide for Generative AI Code Security
Download this guide to explore the processes and tools necessary for effectively leveraging and securing AI-generated code
CISOs Guide to Cultivating Developer Security
This white paper summarizes our learnings from discussions with a variety of organizations that have DevSecOps programs at varying stages of maturity.
The Importance of DevSecOps
Is your organization ready to adopt DevSecOps? Learn the key techniques to embrace a culture of DevSecOps.
How to build a security champions program
Download our playbook to learn how to create a security champions program that works for your organization
Developer Security Tools Buyer’s Guide
This guide discusses all aspects of developer security tools that buyers should consider when looking for a new developer-first security tool.
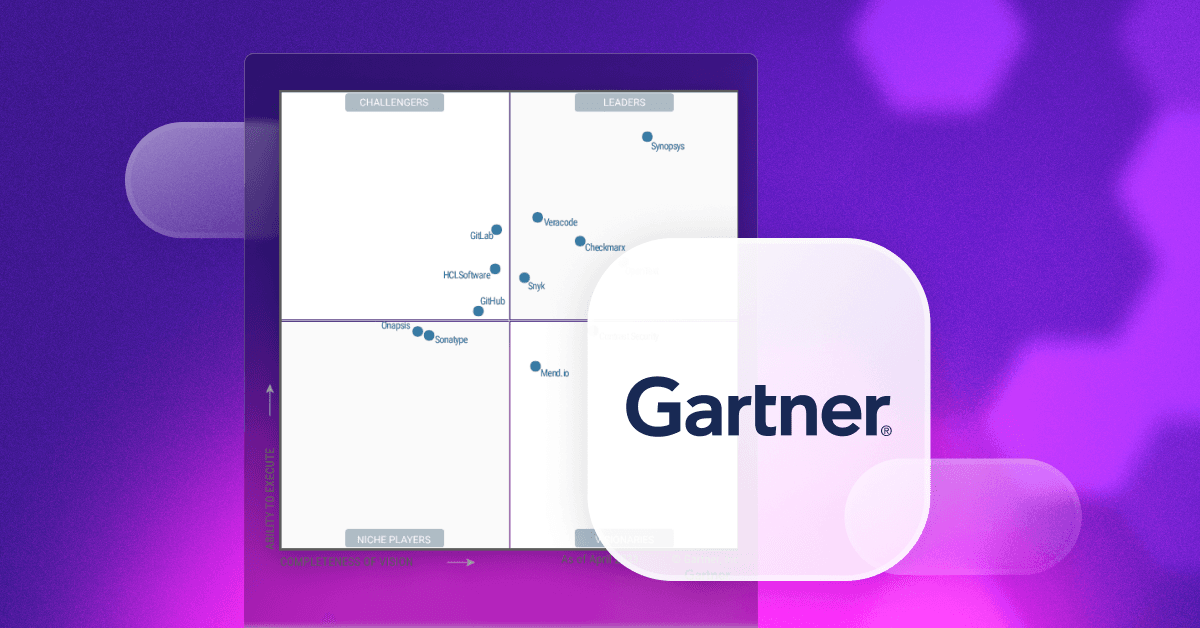
Gartner Magic Quadrant for AST 2023
Get complimentary access to the report for an overview of the Application Security Testing market – and why Snyk is named a Leader.

10 Security Considerations when Migrating to AWS Cheat Sheet
Learn about 10 different ways AWS security considerations you should keep in mind to make the move easy and secure.
DevSecOps Is Just the Beginning: Why Modern Security Teams Need a Transformation (And How They Can Do It)
This playbook explores current inequities between development and security and discusses why modern security teams must shift their role and approach to security integration.
Top considerations when evaluating SAST tools
Download this guide to learn about the key aspects to look out for when choosing your SAST solution.
Guide to Choosing a SAST Solution
Download this guide to learn the recommended 4 phase process for testing & selecting a code security tool.
Start left: your secure cloud journey
In this paper written with Accenture, we’ll help you rethink your Application Security (AppSec) program and processes through the lens of development teams embracing cloud native. We’ll also show you how remediating issues identified by AppSec tools – an area where many developers have been burned in the past – will enable you to build new security processes that will accelerate your journey to the cloud. So read on. You’ll be glad you did.