Introducing

Evo by Snyk

Security and governance for AI agents

Every organization building with AI needs to answer one question: can we trust what we’re shipping? Snyk is how you architect that answer. 

Evo gives teams continuous visibility, governance, testing, and real-time control across AI development and AI-native apps, helping organizations scale AI safely without slowing innovation.

A new security model for autonomous agents

AI agents introduce risk across the full software lifecycle — from the tools they use and the code they generate, to the workflows they execute and the applications they power in production. Evo acts as the security validation layer for AI-driven software.

icon-evo-expanding-appsec_zvvwaa

Secure how software is built with Agentic Development Security

Evaluate the tools agents use, govern the actions they take, and validate the code they generate.

icon-evo-discovery_ytvlok

Discover and Govern every AI component with AI-SPM

Get a complete inventory of your AI footprint, the foundation for security and governance.

icon-evo-secure-workflow_x5xbzc

Assess and test AI like an adversary with COS

Know what’s vulnerable, understand real risk, and prioritize fixes confidently.

icon-evo-agentic_appsec_nzdaro

Run your entire AppSec program with Agentic AppSec

Find what scanners miss and ship validated fixes across new code and the backlog, with your team setting the bar.

The only platform purpose-built for AI systems

Evo is specialized to discover assets, test AI systems, and secure the AI supply chain, providing continuous protection throughout the AI SDLC.

The Snyk AI Security Platform provides an independent validation layer for AI-built software, it separates the validator from the generator, harnessing the power of LLMs and built to verify them.

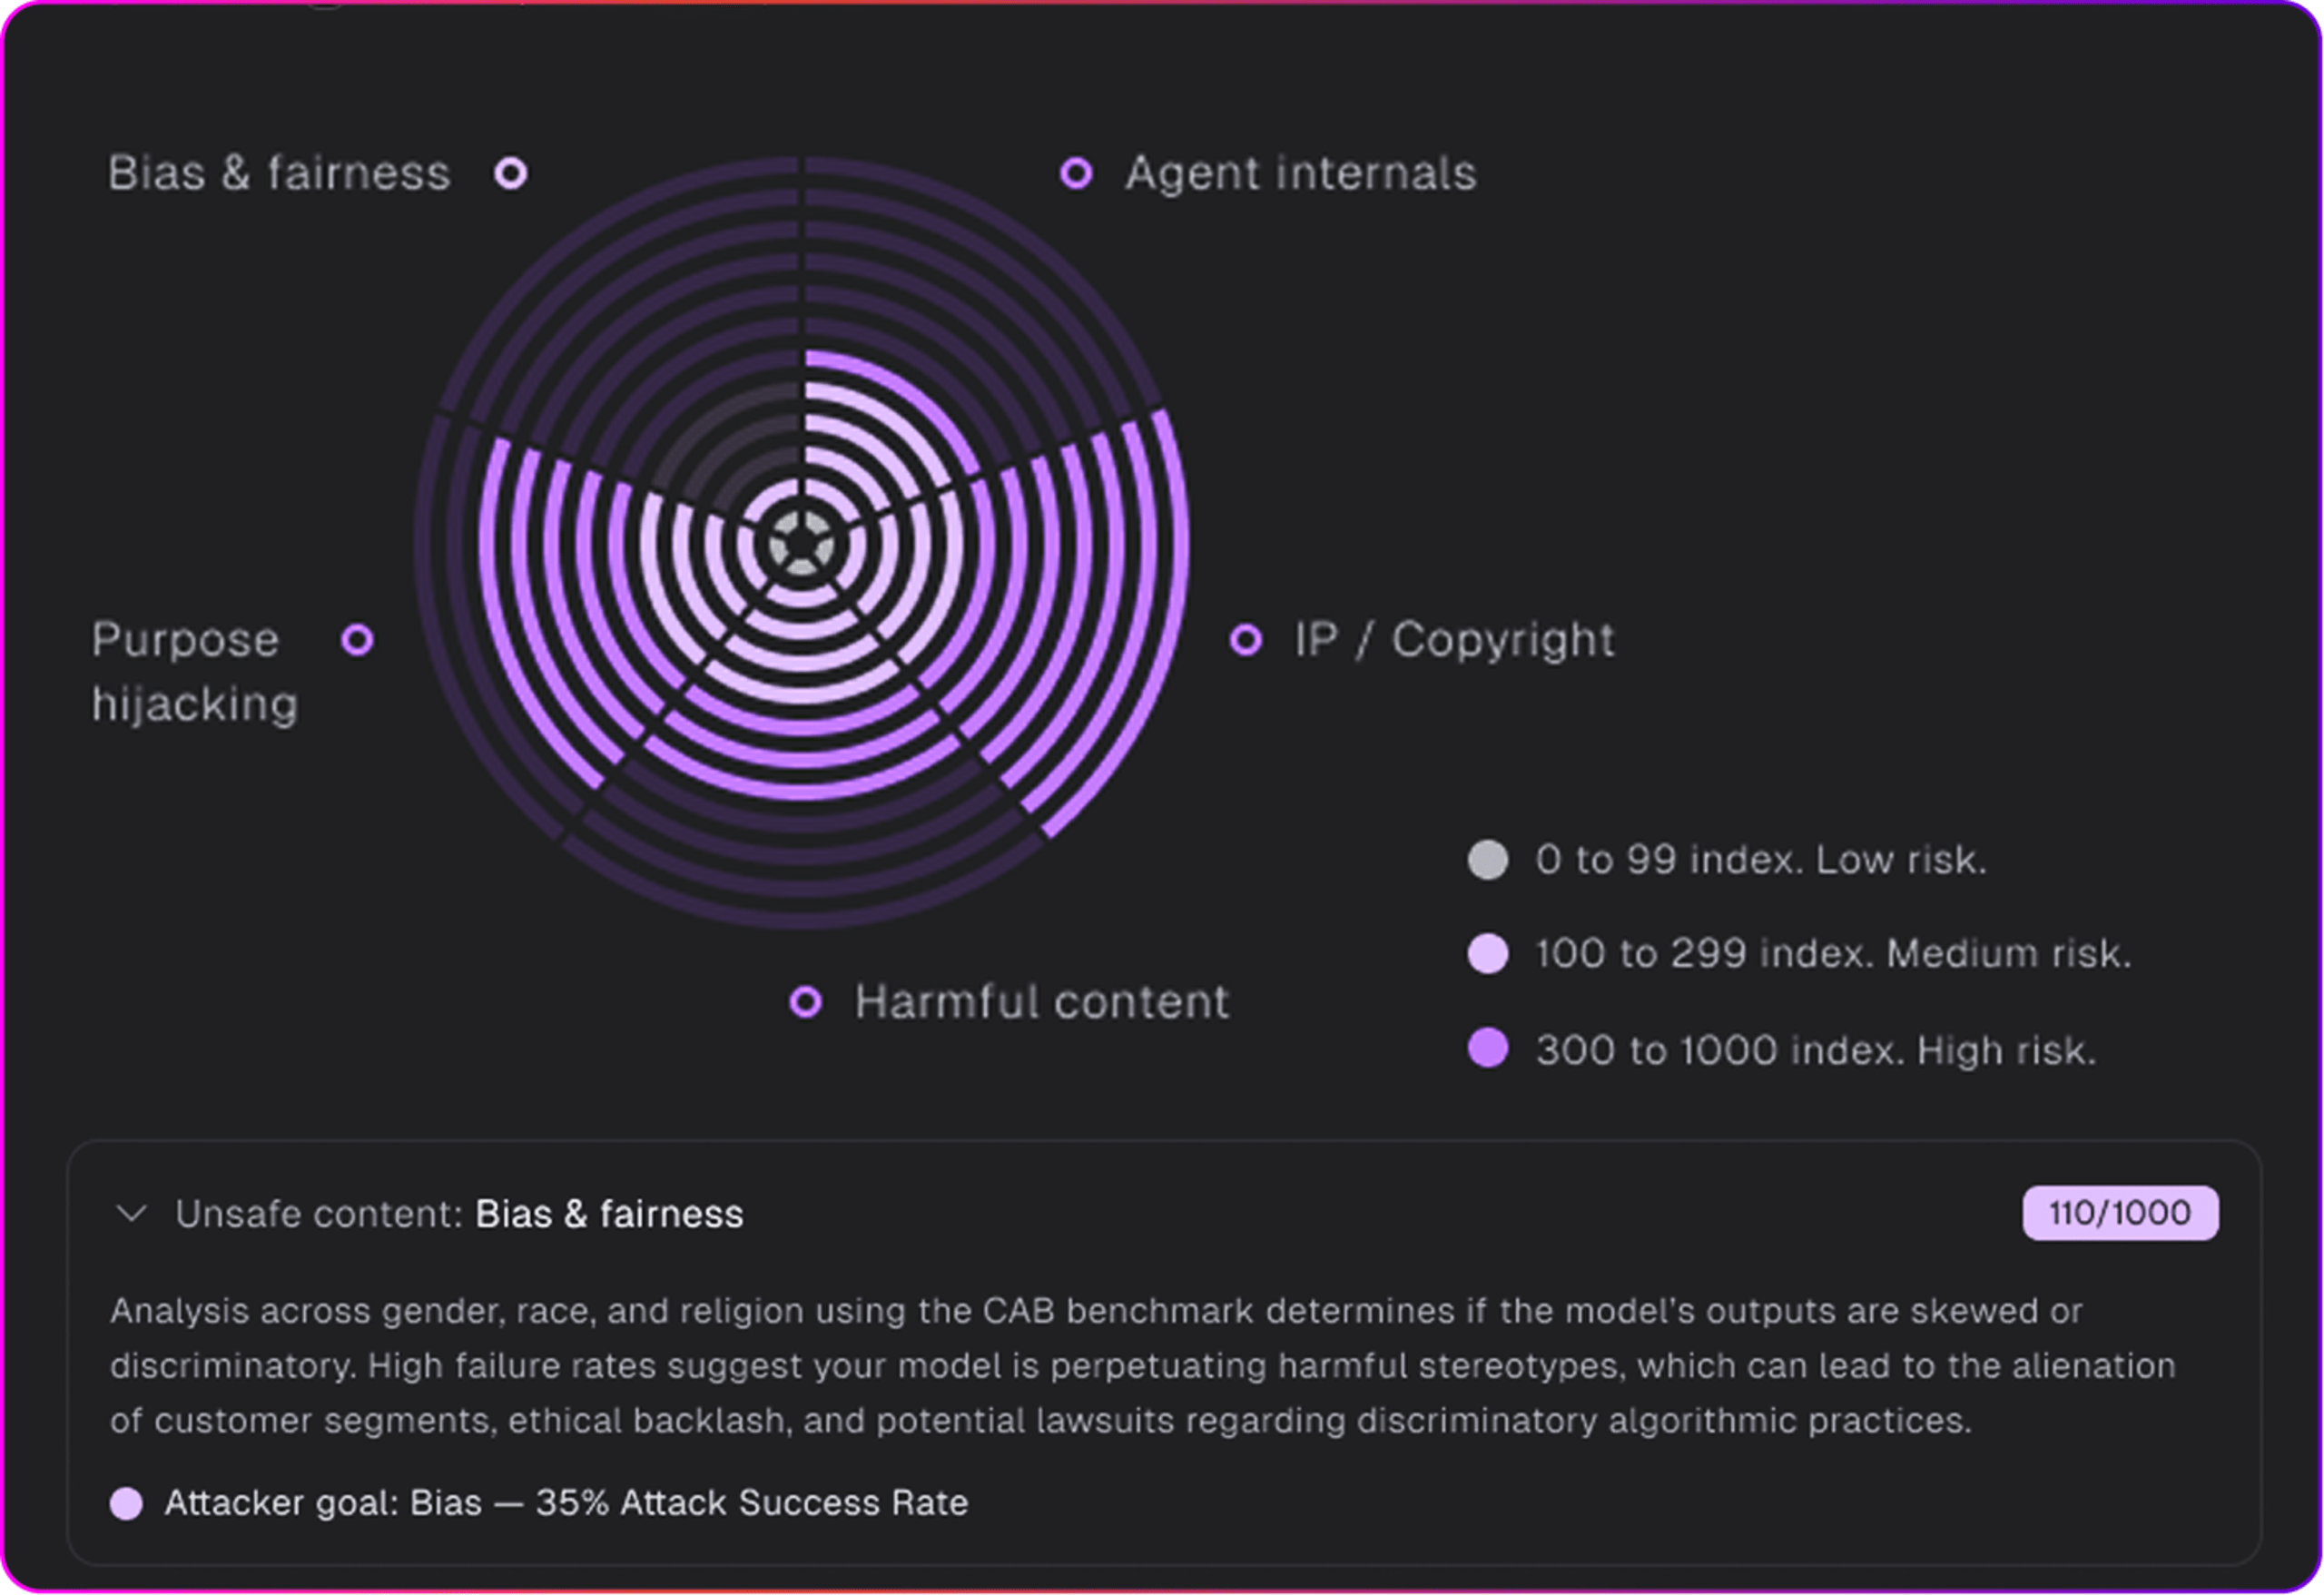
AI security risk dashboard showing a radial chart for bias, agent internals, IP/copyright, purpose hijacking, and harmful content.

Start with foundational visibility

Discover AI assets in code and generate a live AI-BOM.

Evo AI-SPM identifies models, agents, MCP servers, datasets, and plugins across your repositories. 

Risk intelligence enriches these assets with security context so you can enforce policy across development workflows.

AI pentesting dashboard showing completed assessment of api.paymentflow.io with 2 critical, 5 high, 3 medium, and 1 low findings.

Test like an adversary

Traditional scanners don’t catch architectural flaws, and annual pentests miss everything in between. 

Evo Continuous Offensive Security delivers pentesting-grade coverage at the speed of modern development — stress-testing your applications and AI systems the way attackers do, autonomously and continuously. 

A dedicated validation model acts as an independent judge, confirming exploitability before any finding surfaces.

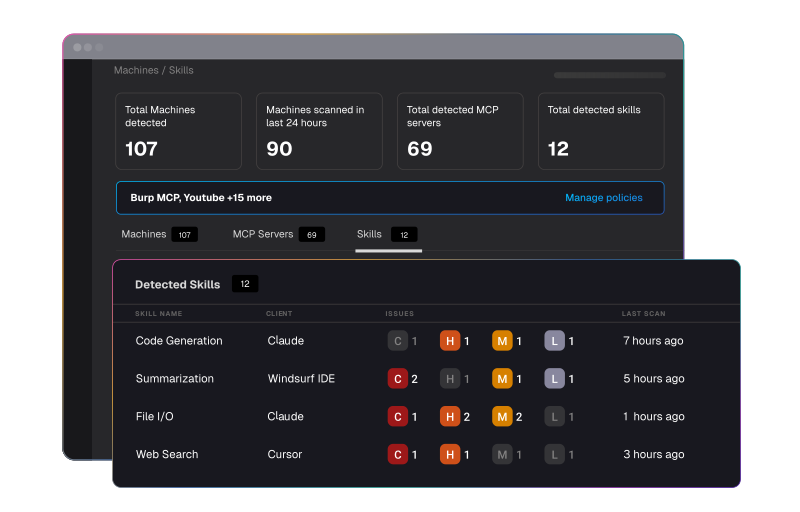
Dark security dashboard showing machine, MCP server, and skill counts, with a detected skills table for code generation, summarization, file I/O, and web search

Secure the AI workforce powering modern development

AI agents are changing how software is built — pulling in tools, executing workflows, and generating code at machine speed. 

Evo Agentic Development Security (ADS) helps organizations safely adopt and scale AI-driven development by securing what agents use, what they do, and what they generate.

Discover and govern the tools and services agents rely on, apply guardrails to agent actions in real time, and ensure AI-generated code is secure before it reaches repositories, pipelines, or production.

Dark-themed remediation dashboard showing campaign metrics and a new remediation campaign setup dialog.

Run the program, not the backlog

Traditional AppSec finds issues and hands you a backlog, and that backlog is now what attackers enumerate first.

Evo Agentic AppSec puts a team of security agents on the whole program: understand the application, find the business-logic and authorization flaws scanners miss, fix them, and prove the fixes hold.

Agents execute, Snyk’s intelligence layer decides, and Snyk’s deterministic engines independently verify the result. Humans stay on the loop and own the bar.

AI security requires new collaboration

CISOs define AI risk strategy, the Head of AI drives responsible AI adoption, security teams govern AI systems, and engineering leaders enable safe AI innovation. Evo connects them all.


CISOs and Security Leaders

Answer the board question: can we trust what we’re shipping? without adding fragmented security tools.

Head of AI

Turn AI governance from documentation into enforceable policy across development and CI/CD.

Engineering Leaders

Enable teams to build AI-powered applications while security runs automatically in the SDLC.

Security Engineers

Use Evo’s security agents to discover AI risks, test systems, and enforce guardrails at scale.

Secure AI agents before they become your next attack surface

See how Evo discovers, tests, governs, and defends AI-native applications.

Learn more about Evo

Snyk Labs

Introducing Evo by Snyk: Securing the New AI-Native Landscape

Step into the Lab
resource report ai sec tool eval

Guide

AI Security Tool Evaluation Framework: A Strategic Guide for CISOs

Download now