1❯ export DOCKER_CONTENT_TRUST=12❯ docker push myaccount/myimage:1 3The push refers to repository [docker.io/myaccount/myimage]464ab2aa20cf9: Layer already exists 5b99937123ca0: Layer already exists 6…7orig: digest: sha256:c221d4dc80b8a0d3866602020b09722d942157c720273d325a0496a529b5fcab size: 40938Signing and pushing trust metadata9You are about to create a new root signing key passphrase. This passphrase10will be used to protect the most sensitive key in your signing system. Please11choose a long, complex passphrase and be careful to keep the password and the12key file itself secure and backed up. It is highly recommended that you use a13password manager to generate the passphrase and keep it safe. There will be no14way to recover this key. You can find the key in your config directory.15Enter passphrase for new root key with ID 85871b5: 16Repeat passphrase for new root key with ID 85871b5: 17Enter passphrase for new repository key with ID e675351: 18Repeat passphrase for new repository key with ID e675351: 19Finished initializing "docker.io/ericsmalling/javagoof"20Successfully signed docker.io/myaccount/myimage:121
❯ docker run --rm -it myaccount/someapp docker: Error: remote trust data does not exist for docker.io/myaccount/someapp: notary.docker.io does not have trust data for docker.io/myaccount/someapp.See 'docker run --help'.
❯ `Generate keypair (do this once):❯ cosign generate-key-pair Enter password for private key: Enter password for private key again: Private key written to cosign.keyPublic key written to cosign.pub❯ `Sign the already-pushed image❯ cosign sign --key cosign.key myaccount/myimage:1 Enter password for private key: tlog entry created with index: 1234567Pushing signature to: index.docker.io/myaccount/myimage
❯ export COSIGN_EXPERIMENTAL=1❯ cosign sign myaccount/myimage:1Generating ephemeral keys...Retrieving signed certificate... Note that there may be personally identifiable information associated with this signed artifact. This may include the email address associated with the account with which you authenticate. This information will be used for signing this artifact and will be stored in public transparency logs and cannot be removed later. By typing 'y', you attest that you grant (or have permission to grant) and agree to have this information stored permanently in transparency logs.Are you sure you want to continue? (y/[N]): yYour browser will now be opened to:https://oauth2.sigstore.dev/auth/auth?access_type=online&client_id=sigstore&code_challenge=********************Successfully verified SCT...tlog entry created with index: 1234567Pushing signature to: index.docker.io/myaccount/myimage
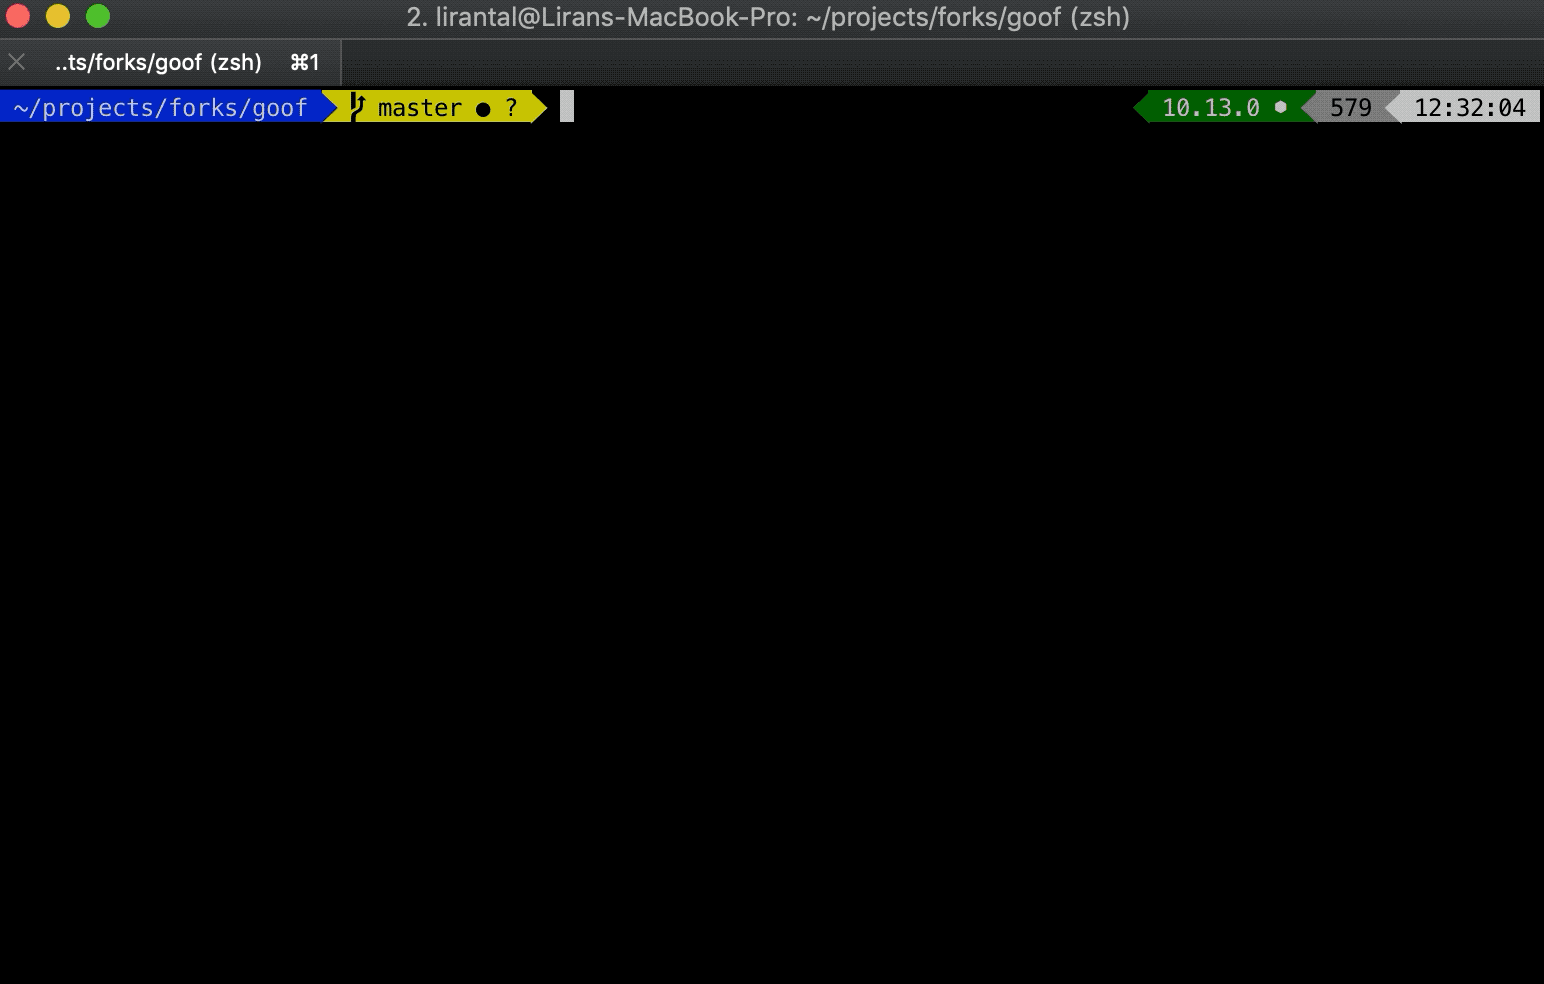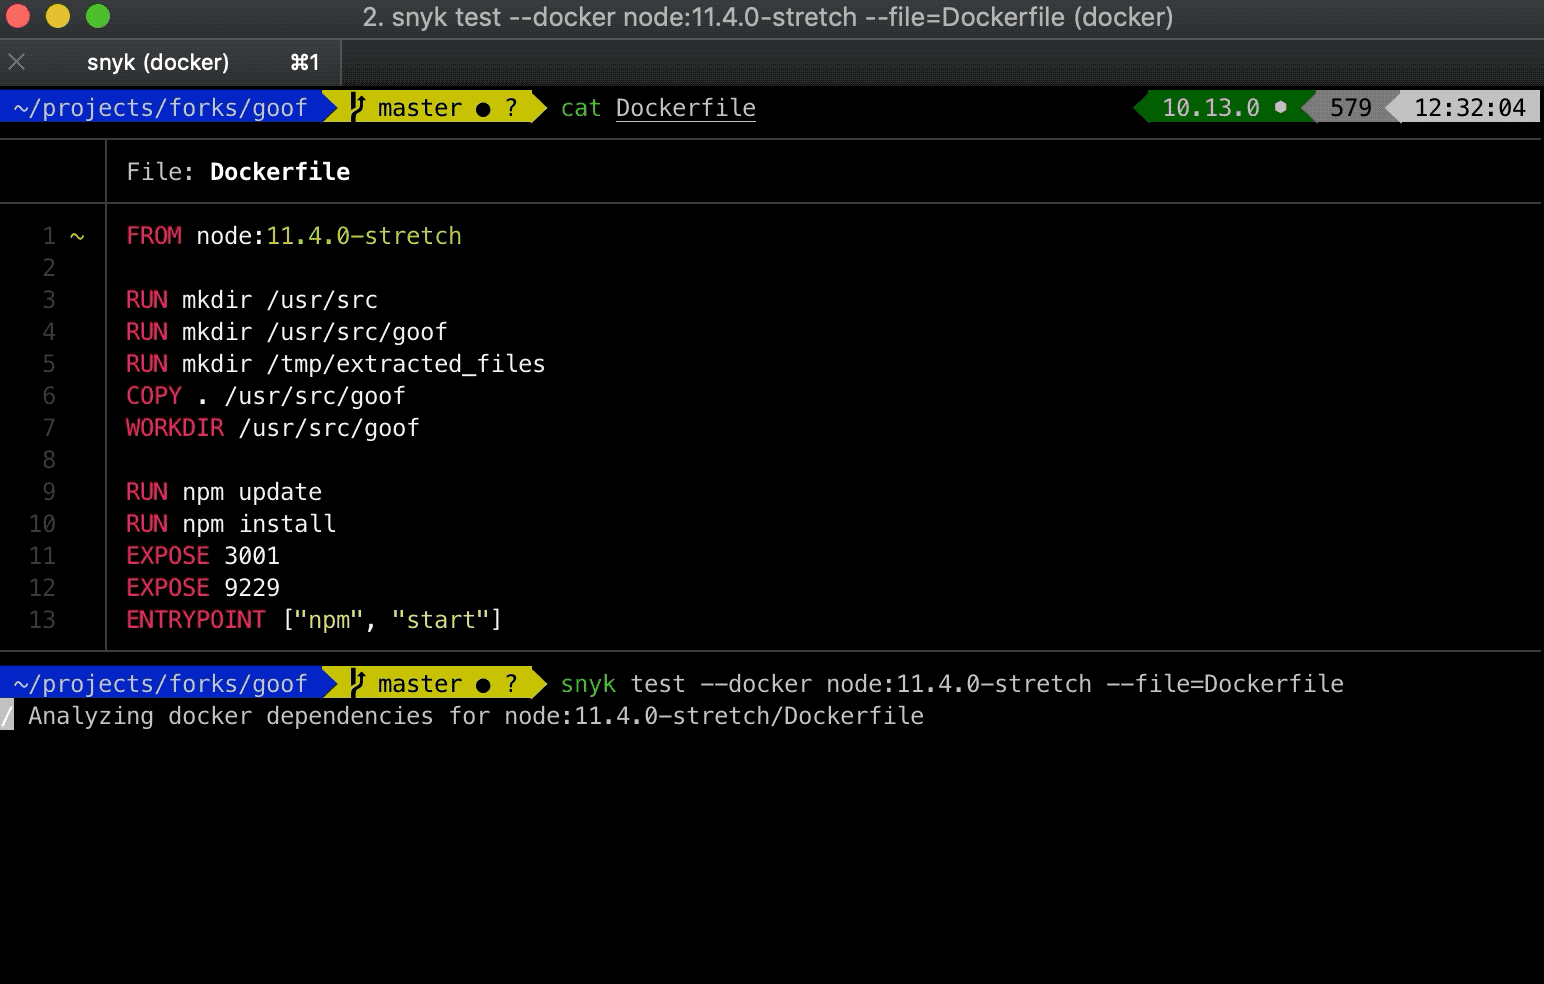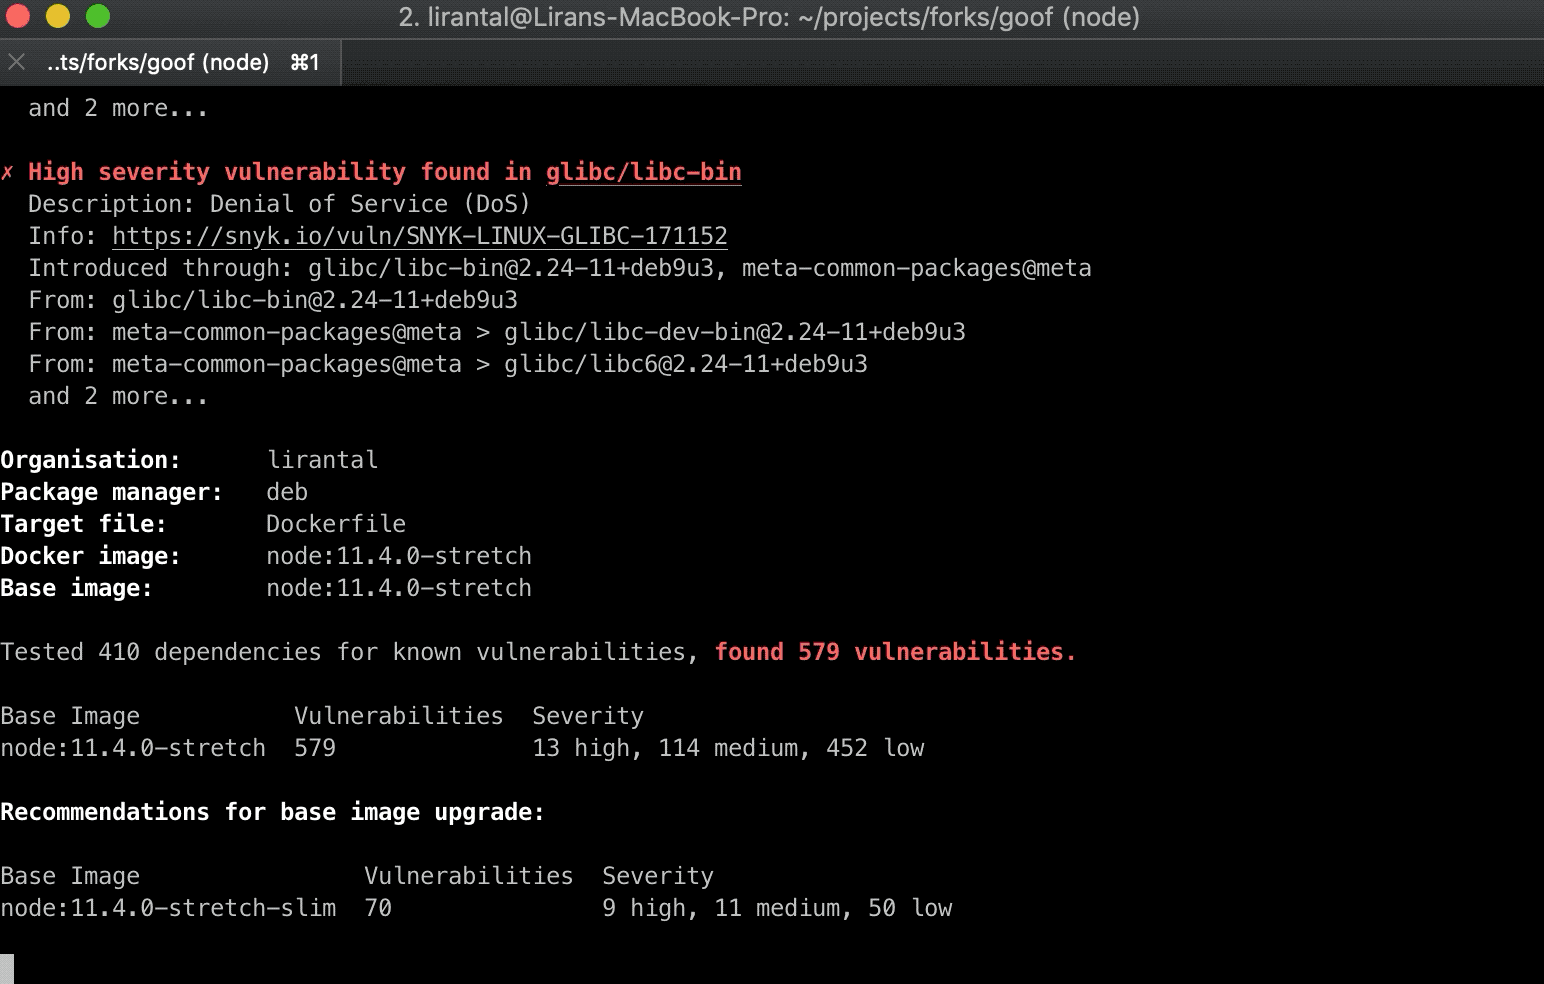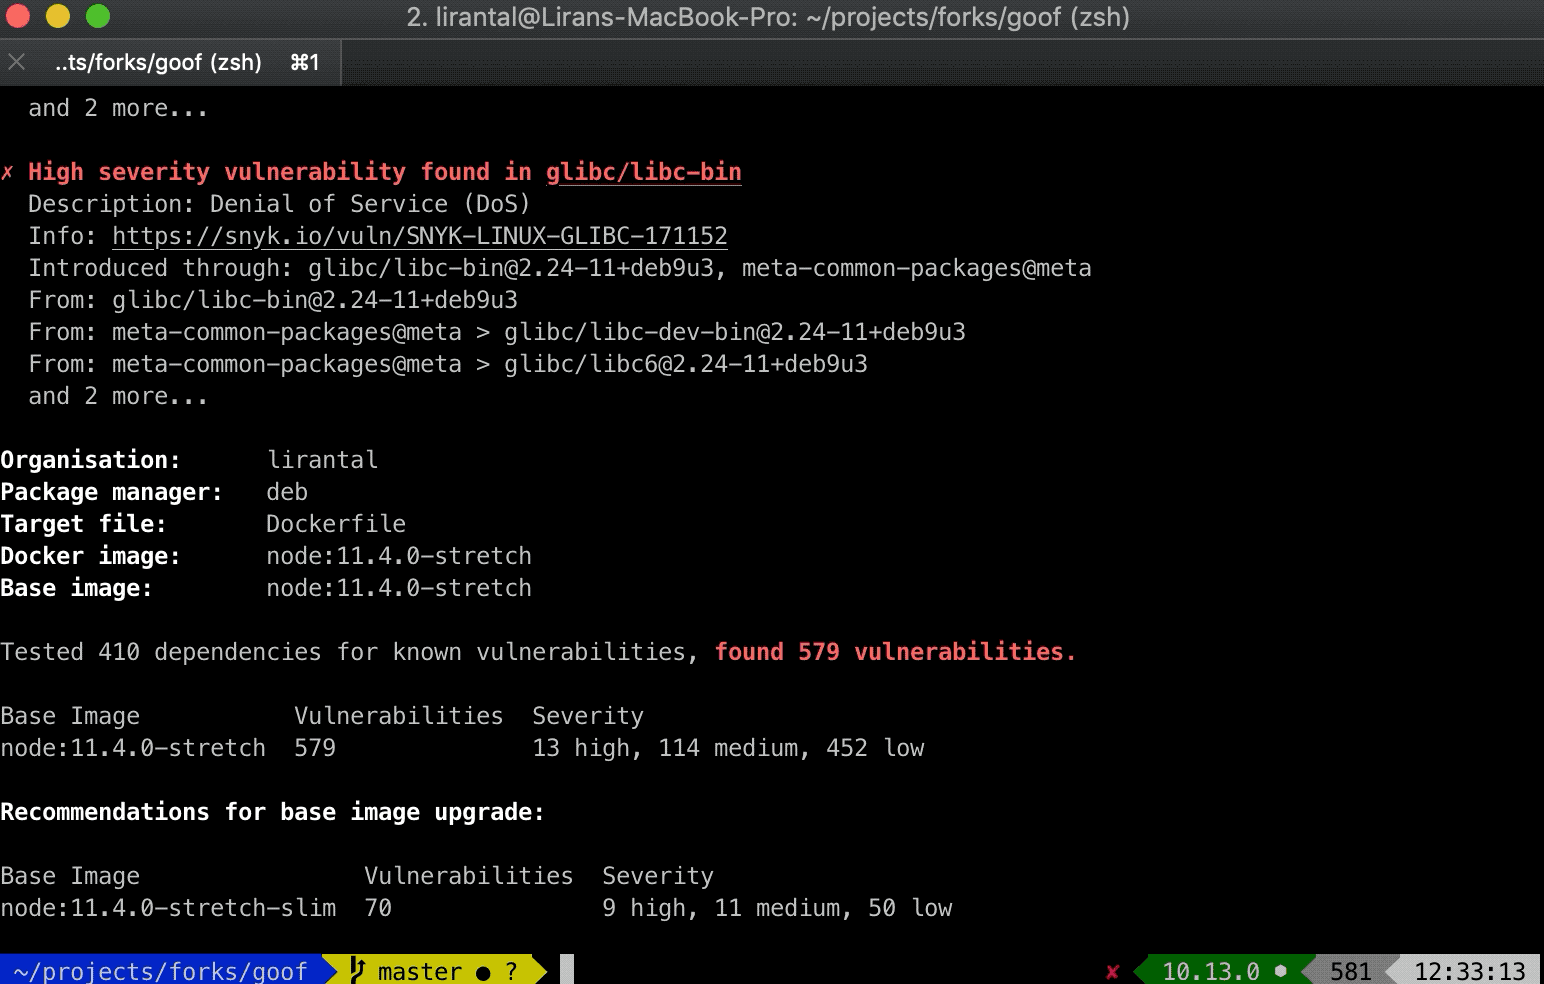
1# fetch the image to be tested so it exists locally2$ docker pull node:103# scan the image with snyk4$ snyk test --docker node:10 --file=path/to/Dockerfile
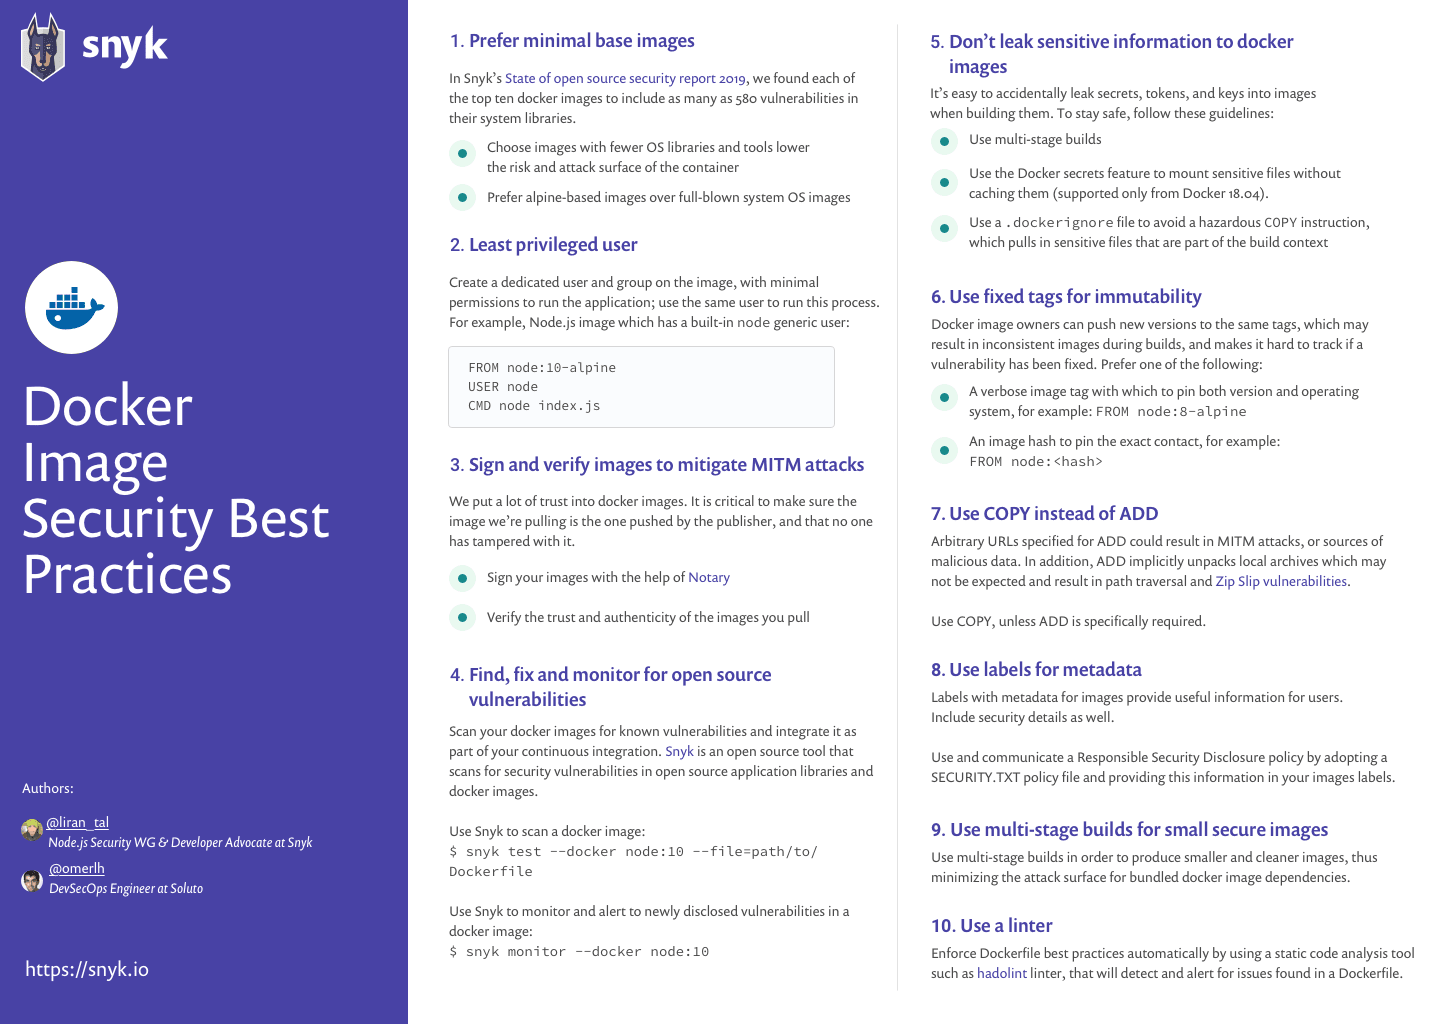
Dockerセキュリティのベストプラクティスに従い、既知の脆弱性が少ない、またはないDockerベースイメージを使用し、Dockerfileのセキュリティ設定を適切に行いましょう。また、デプロイ済みのコンテナを監視して、開発環境と本番環境でイメージに差異が生じていないことを確認してください。さらに、コンテナオーケストレーションソリューションでもInfrastructure as Codeのベストプラクティスに従いましょう。