Monitoring open source packages at runtime - now in open beta

Aner Mazur
January 30, 2019
0 mins readToday we’re delighted to share that we’re launching our Open Source Security Runtime Monitoring solution, in beta, to all users, with no limitation on usage!
While Snyk invests heavily in making fixing vulnerabilities ridiculously easy by baking it into the development workflow, handling a large backlog of issues can be time-consuming.
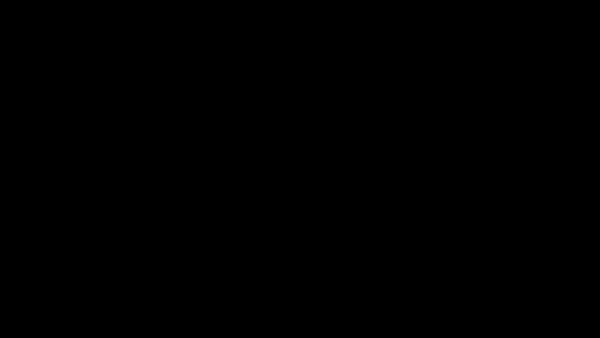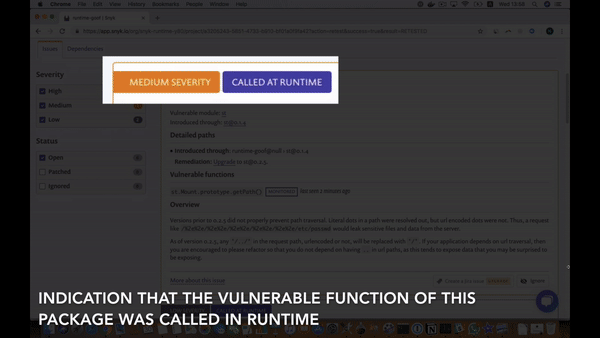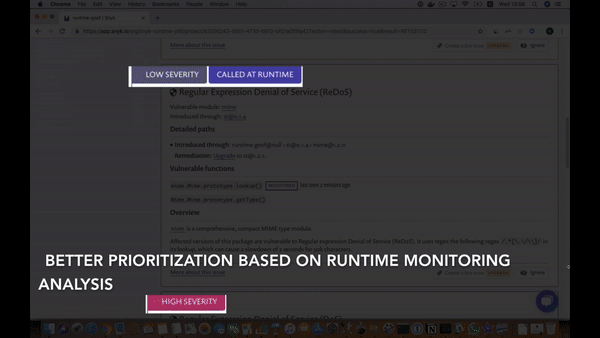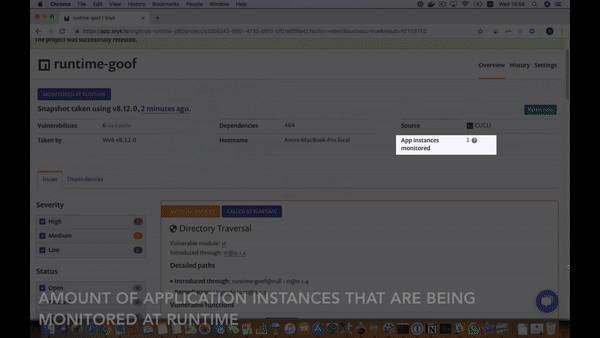
We’ve spent the past few months building runtime monitoring, a solution that will help you automatically prioritize these vulnerabilities. Snyk now determines whether a vulnerable dependency is being used at runtime in a way that can be exploited.
Take a quick look into the UI feedback you’ll see once Snyk runtime monitoring is successfully analyzing your project for vulnerable functions:
How runtime monitoring works
A low overhead agent instruments all vulnerable functions in the project’s dependencies and detects actual invocations of the vulnerable functions at runtime.
Rest assured that keeping any performance impact to an absolute minimum has been a priority throughout the development of this feature, and we keep testing that. As part of being fully transparent regarding what you’ll be running in runtime, we’ve made the agents themselves open source. Take a look at our node agent and java agent code.
Find out more
For more information on our runtime monitoring solution and instructions for getting started, visit our previous blog post about runtime monitoring, and read our Documentation.
The instrumentation of the application at runtime opens up many more security capabilities on top of the runtime-based vulnerability prioritization released today. We’ll be sharing these in the coming months, so stay tuned! :)


