Discover package vulnerabilities with the Snyk integration for JSDelivr

June 8, 2020
0 mins readWe are excited to announce that we power the security badge in JSDelivr.com!
JSDelivr is one of the leading CDN for open source and npm packages. Snyk’s new integration with JSDelivr shows a security badge on the search page for a specific library.
At Snyk, we strongly believe that it is important for developers to choose carefully the packages their code depends on, without sacrificing their delivery pace. The JSDelivr integration does just that by helping developers deliver faster, better, and more secure software from the start.
See if a specific version of a package has a security issue immediately when searching on the JSDelivr website. The Snyk integration links to the specific vuln page on the Snyk website, offering a better view of the issue(s).
How does it work
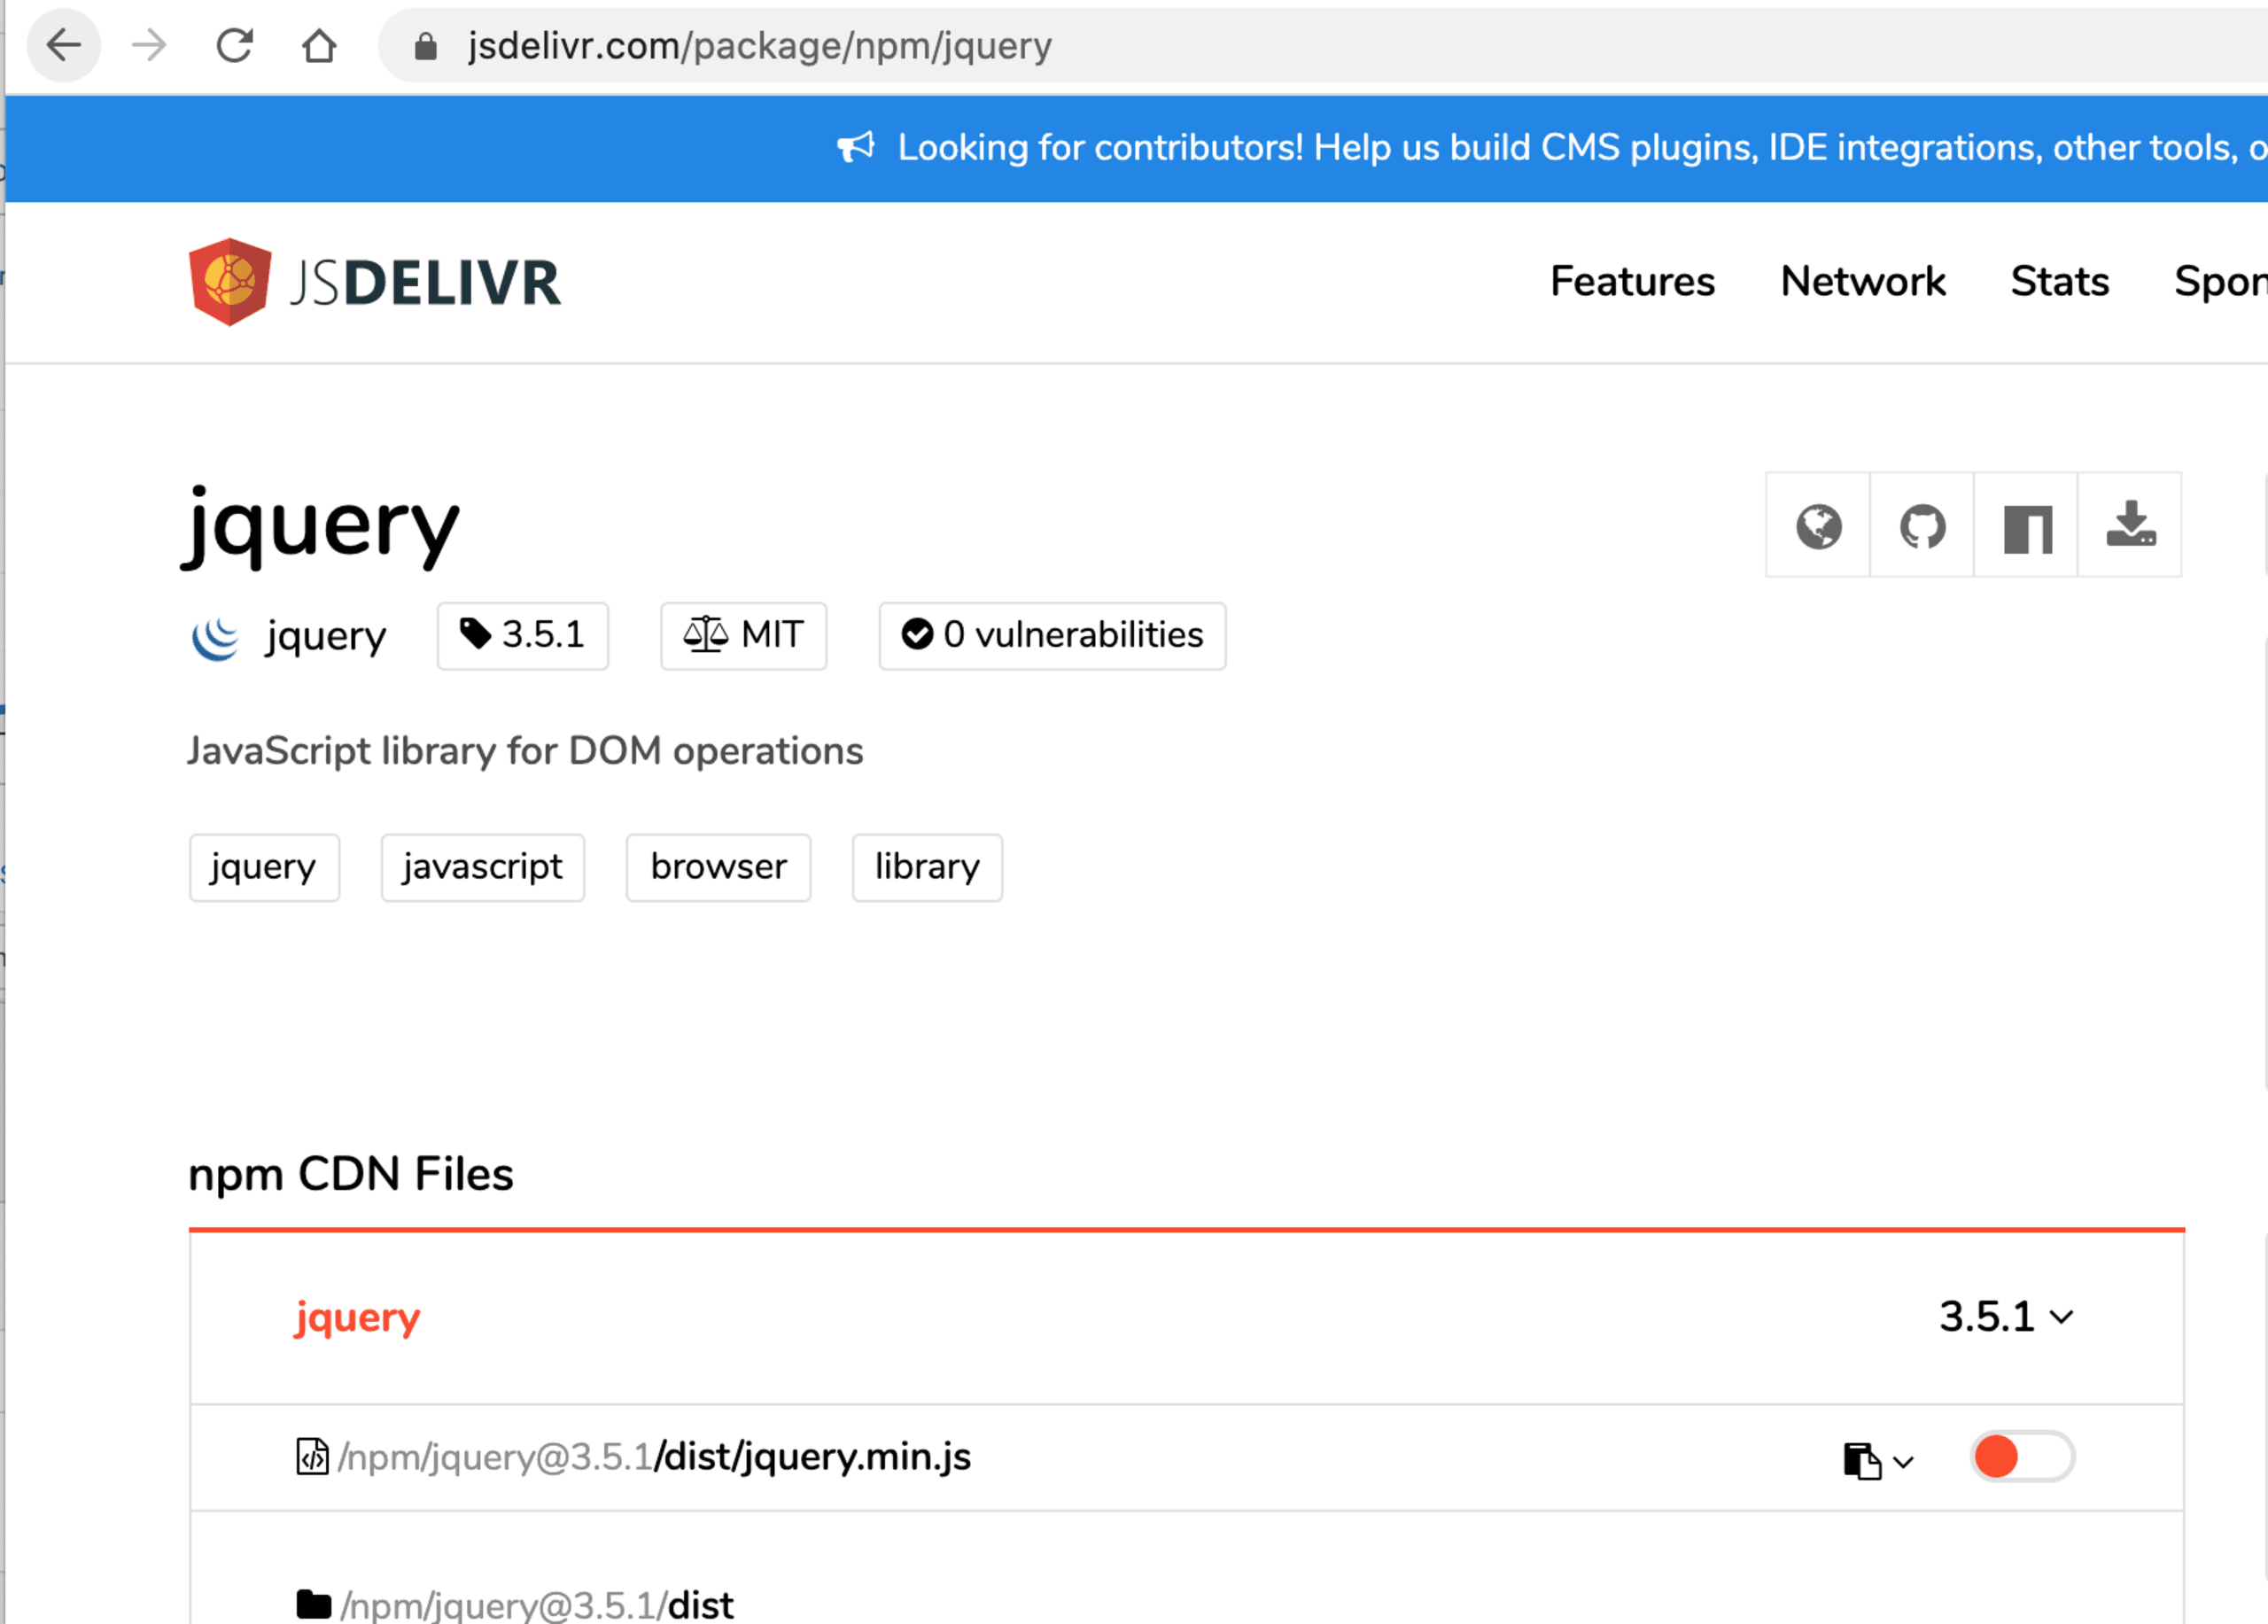
When searching for npm packages on JSDelivr, a security badge appears with the number of vulnerabilities this package has. Looking at jQuery, for example, the current version (3.5.1 at the time of writing) does not have any issues.
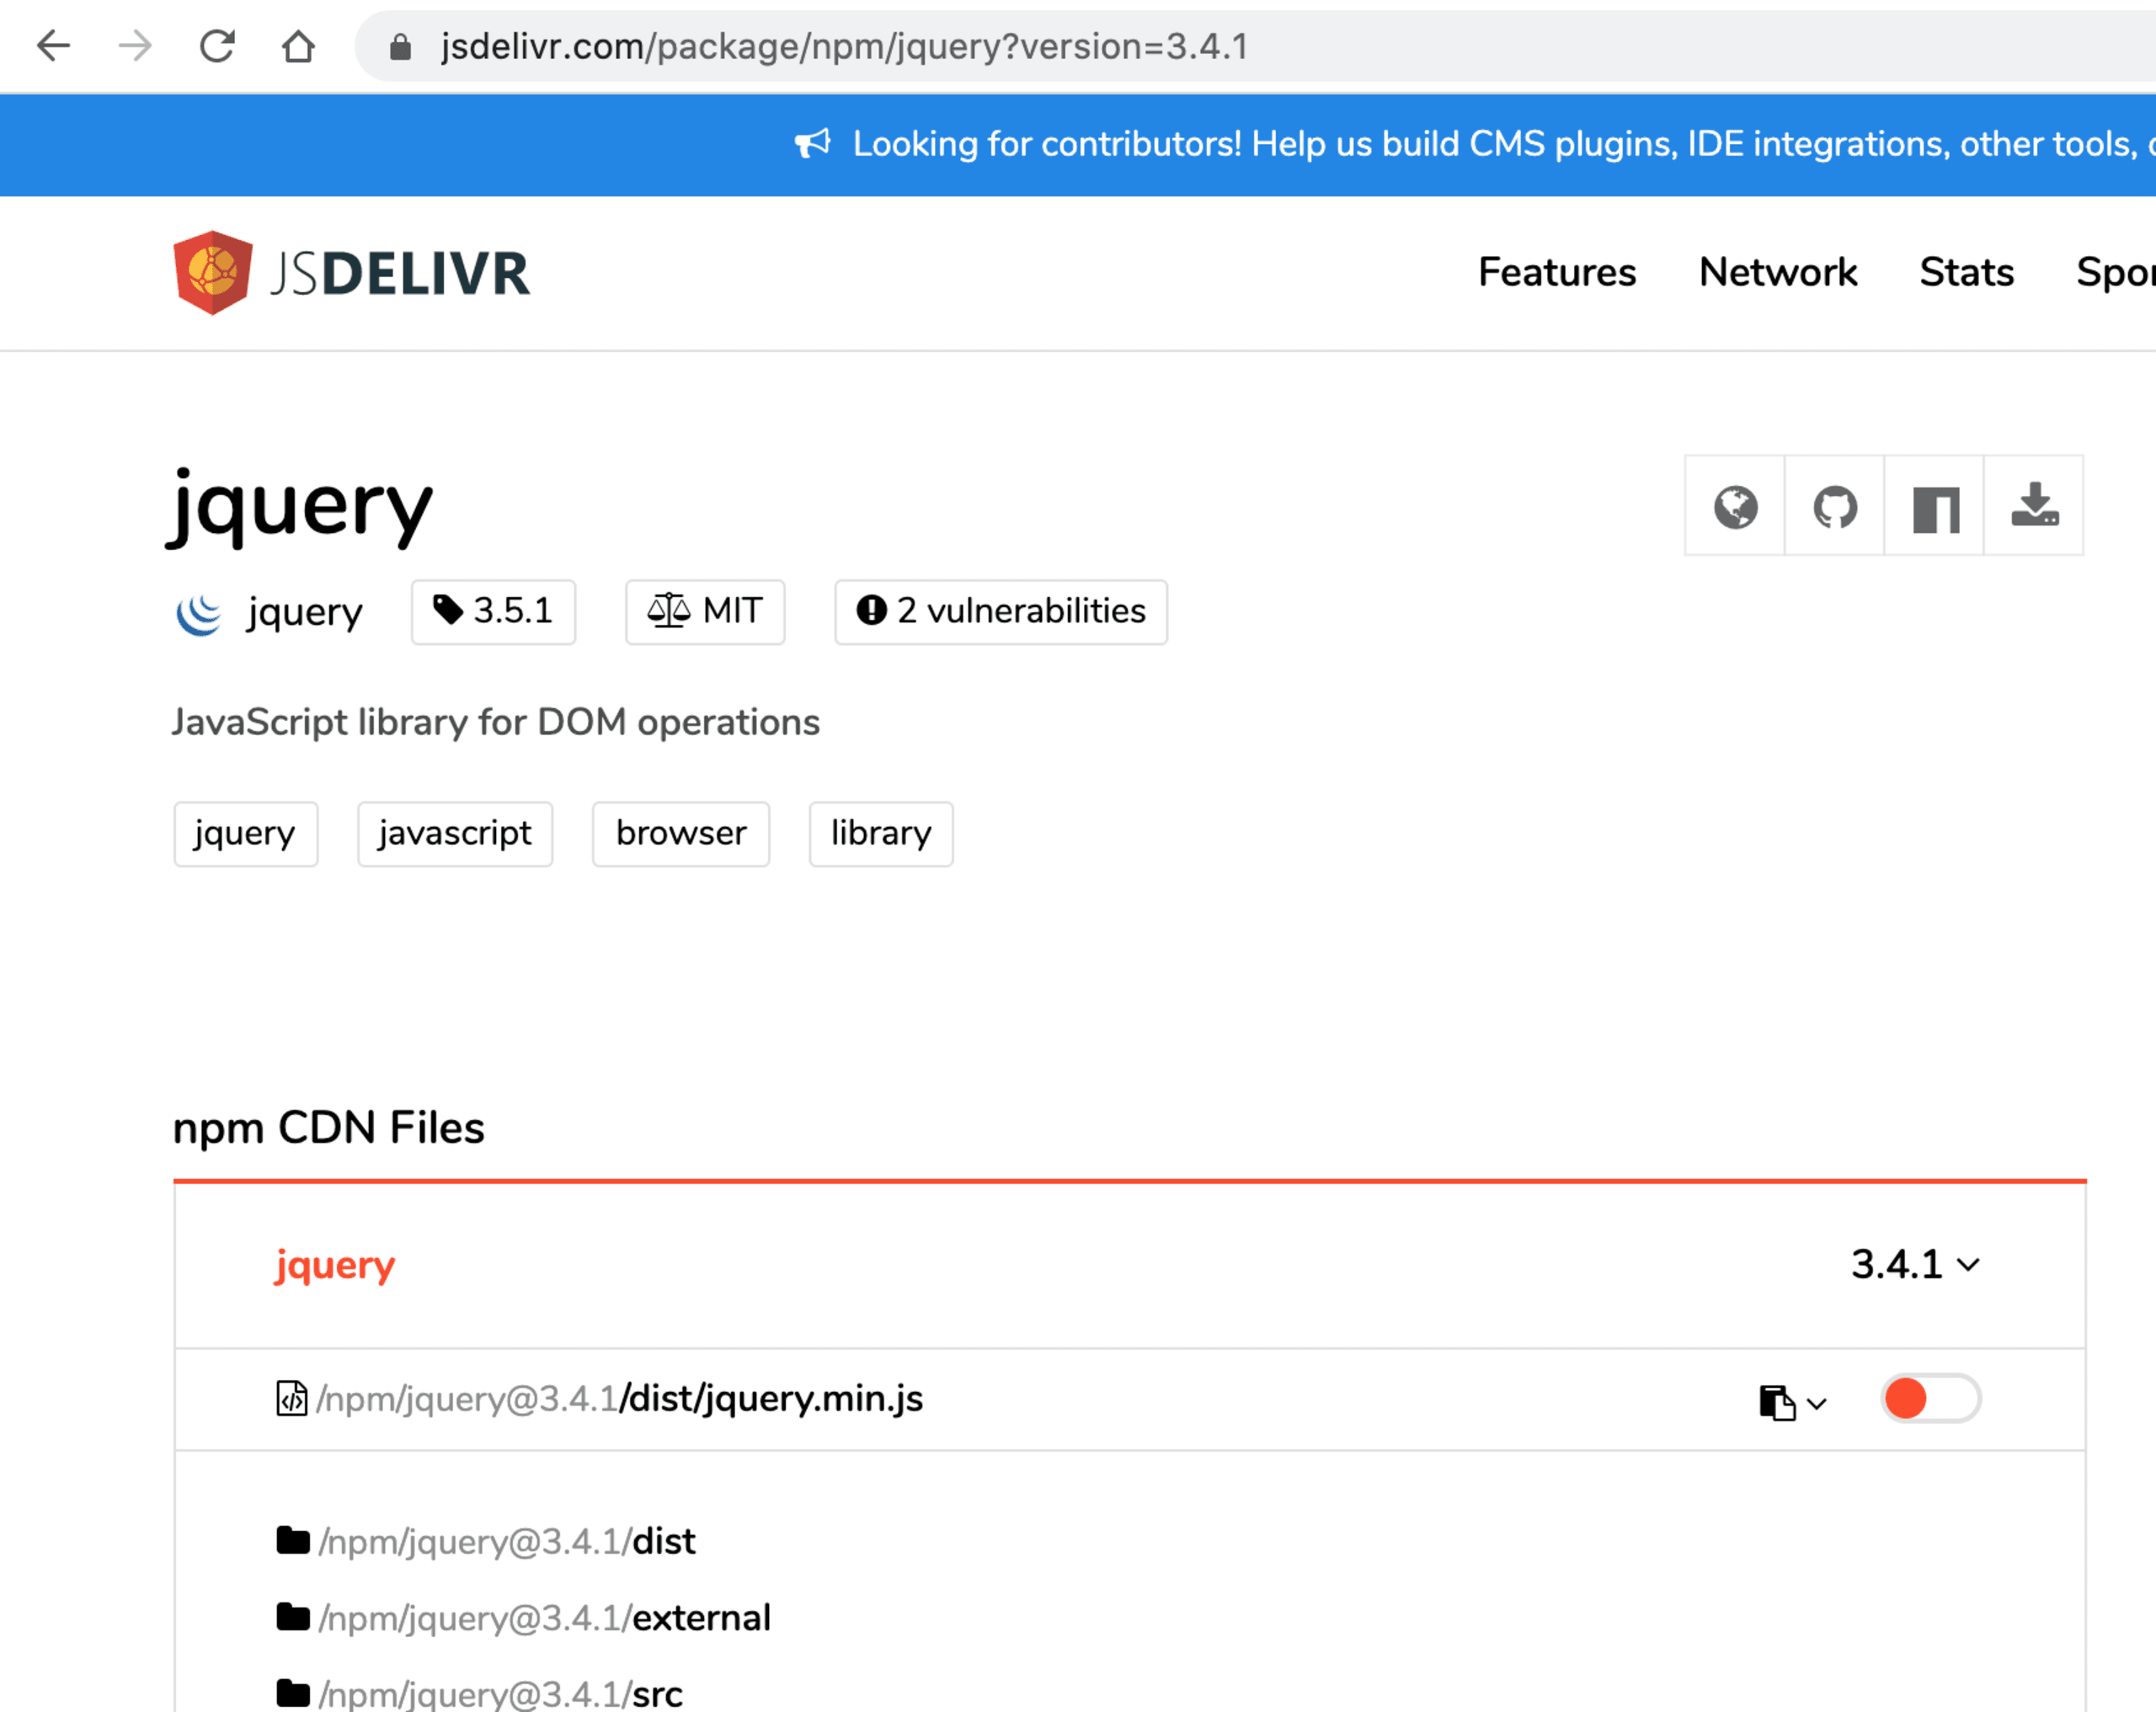
When changing the version to 3.4.1, you immediately see the badge changing to “2 vulnerabilities”. When you click on the badge, it opens the Snyk vulnerability page for this specific version of the library that offers more insights on the individual issues.
Our goal with this integration is to offer our security knowledge in order to make it easier for developers to react accordingly to security issues.
But don’t forget that you can always create a free Snyk account to keep your open source projects secure by using our expert security insights! Why not try it now?
Get started in capture the flag
Learn how to solve capture the flag challenges by watching our virtual 101 workshop on demand.


