Real-time code scanning and auto-fixing
No more waiting for SAST reports. Scan, and automatically remediate source code issues with pre-screened fixes in seconds to minutes, build-free in the IDE and pull requests.
Insecure code is at the forefront of application security. With Snyk Code, your developers can find insecure code fast with integrations across their entire SDLC.
“Snyk Code gave us a net new capability to add to our arsenal. It analyzes code we write, quickly, and provides legitimate, actionable information that engineers can use during development and within build workflows. The Snyk view lets engineers quickly see any code issues, other sources for that issue, as well as how other engineers in the industry have fixed the issue. It gives us meaningful static analysis results that we can take action on immediately.”

Joren McReynolds
Director of Engineering, Panther Labs
Prevent code delays with fix advice and automatic fixes backed by industry-leading security intelligence.
Get real-time, in-line results with complete, automatic scans and 80%-accurate fixes, in your IDE and pull requests.
Find code vulnerabilities, understand more with dev-friendly context-specific explanations, and instantly apply auto-fixes with one click.
Snyk Code was the only AI-powered code security tool shortlisted by developers in Stack Overflow’s 2024 survey. Get the security intelligence and remediation advice you need without disrupting the development workflow.
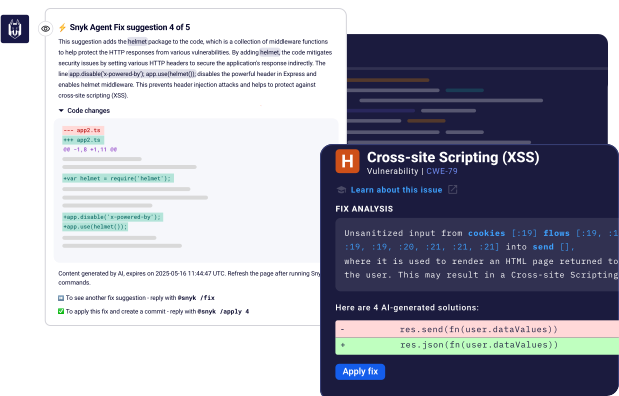
No more waiting for SAST reports. Scan, and automatically remediate source code issues with pre-screened fixes in seconds to minutes, build-free in the IDE and pull requests.

Snyk’s vulnerability scanner is compatible with most popular languages, IDEs, and CI/CD tools — and our coverage is constantly expanding, including our source libraries, encompassing 90% of all LLM libraries like OpenAI and Hugging Face, amongst others.

With 25M+ data flow cases modeled, Snyk’s powerful machine learning engine combs millions of open source libraries, helping human-in-the-loop AI build our robust knowledge base — ensuring cutting-edge security tooling.
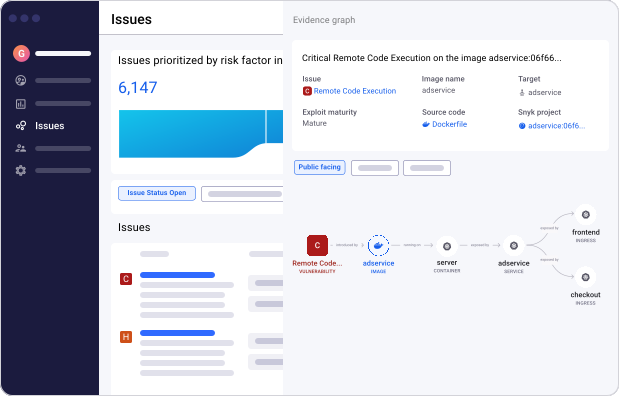
Snyk’s code vulnerability detection leverages broad application context and adaptable features to eliminate noisy results and prioritize new, deployed, or publicly exposed code issues that are riskier or more relevant to your organization.
Millions of developers build securely with Snyk


Snyk fits seamlessly into your existing toolchain across IDEs, repositories, and CI/CD pipelines, making it easy to embed open source security into every stage of development.